Florida’s technology economy is undergoing an unprecedented boom. From the international banking towers and fintech accelerators of Miami and Brickell, to the aerospace and simulation defense corridor stretching across Orlando and the Space Coast, to the burgeoning healthcare and wealth management headquarters in Tampa Bay and St. Petersburg, Florida has firmly established itself as one of the premier business hubs in the United States.
With this explosive growth comes significant cybersecurity risk. According to the FBI’s Internet Crime Complaint Center (IC3), Florida consistently ranks in the top three states nationwide for cybercrime financial losses. Between stringent state data privacy laws like the Florida Information Protection Act (FIPA), aggressive enforcement from the FTC, and strict audit mandates for SOC 2 Type II, HIPAA, PCI DSS 4.0, and CMMC 2.0, hiring the right penetration testing firm has become a mission-critical governance decision.
However, navigating the crowded marketplace of pentesting companies in Florida is daunting. Florida buyers face a confusing array of options: bloated legacy consulting firms charging six-figure fees, regional IT resellers masquerading as security specialists, automated scan vendors peddling raw Nessus dumps, and modern continuous Penetration Testing as a Service (PTaaS) platforms. This guide provides an honest, empirical evaluation to help Florida security leaders select the ideal penetration testing partner.
Florida’s Regulatory & Compliance Landscape in 2026
Before evaluating vendors, it is essential to understand the specific legal and regulatory demands placed on organizations operating within the state of Florida:
1. The Florida Information Protection Act (FIPA - FL Stat. § 501.171)
Florida’s primary data breach statute mandates that commercial entities maintaining personal information must take reasonable measures to protect that information from unauthorized acquisition. If a breach occurs due to an unaddressed vulnerability that should have been identified through standard security testing, organizations face strict 30-day reporting windows to the Florida Department of Legal Affairs and civil penalties of up to $500,000. Independent penetration test reports provide defensible legal evidence that your organization met its statutory duty of care.
2. SOC 2 Type II & Enterprise B2B Vendor Due Diligence
For Florida SaaS companies and technology providers selling to enterprise clients in New York, California, or London, vendor security assessments demand an annual external penetration test conducted by certified ethical hackers. Point-in-time automated scans are unilaterally rejected by SOC 2 auditors.
3. Healthcare Networks & HIPAA Security Rule (§ 164.308(a)(8))
With massive healthcare networks anchored in Tampa, Orlando (Lake Nona Medical City), and South Florida, healthcare providers handling electronic Protected Health Information (ePHI) require rigorous technical penetration testing across web portals, patient APIs, and internal cloud infrastructure.
4. Defense Industrial Base & CMMC 2.0
Central Florida and the Space Coast host thousands of Department of Defense (DoD) contractors and aerospace ventures. Meeting CMMC 2.0 Level 2 and NIST SP 800-171 mandates requires verified vulnerability remediation and offensive testing across Controlled Unclassified Information (CUI) boundaries.
How to Evaluate Pentesting Companies in Florida
When selecting a penetration testing vendor in Florida, savvy CISOs and engineering leaders look beyond flashy marketing and evaluate four objective criteria:
- Methodology & Proof-of-Concept Verification: Does the vendor perform deep manual exploitation (OWASP Top 10, business logic flaw identification, authorization bypass, DAG exploit chaining), or do they simply run an automated scanner and rebrand the output as a PDF report?
- Retest Policy & Hidden Fees: Traditional consultancies bill an extra $2,500 to $5,000 for retesting fixed vulnerabilities or require an entirely new Statement of Work (SOW). Elite PTaaS providers include unlimited 1-click retest verifications at zero additional cost.
- Turnaround Time & Velocity: Can the firm begin testing within days and deliver auditor-ready findings within 72 hours, or do they require a four-week calendar lead time followed by a month-long wait for a static PDF?
- Developer Integration: Does the vendor deliver findings directly into Jira, GitHub, or developer IDEs with reproducible cURL scripts, or do your engineers have to manually copy-paste screenshots out of a 70-page document?
Top Penetration Testing Providers Serving Florida: Detailed Comparison
| Provider Category | Typical Cost | Retest Fee | Turnaround | Audit Acceptance | Best For |
|---|---|---|---|---|---|
| Lorikeet Security (Talon PTaaS) | $1,999 – $9,999 / yr | $0 (Unlimited Included) | 72 Hours SLA | 100% Accepted (SOC 2, ISO, HIPAA, PCI) | High-growth tech, SaaS, fintech & enterprise teams |
| Big Four Consultancies (Deloitte, PwC, EY) | $35,000 – $75,000+ | $5,000+ SOW Change Order | 6 – 9 Weeks | 100% Accepted | Fortune 500 banks & state government agencies |
| Legacy National Consultancies (Crowe, Protiviti, RSM) | $15,000 – $35,000 | $2,500 – $4,000 | 4 – 6 Weeks | 100% Accepted | Mid-market manufacturing & legacy enterprise |
| Local Florida Regional IT Boutiques | $10,000 – $22,000 | $2,000 – $3,500 | 3 – 5 Weeks | Variable (depends on staff) | Local SMBs seeking on-site office testing |
| Automated Vulnerability Scanners (Nessus, Qualys) | $4,000 – $12,000 licence | N/A (Automated rerun) | Instant (Raw Dump) | 0% Accepted for Pentest Audits | Internal vulnerability patch hygiene only |
Deep Dive: 3 Leading Approaches to Florida Pentesting
1. Modern Continuous PTaaS: Lorikeet Security (Talon PTaaS + Lory AI)
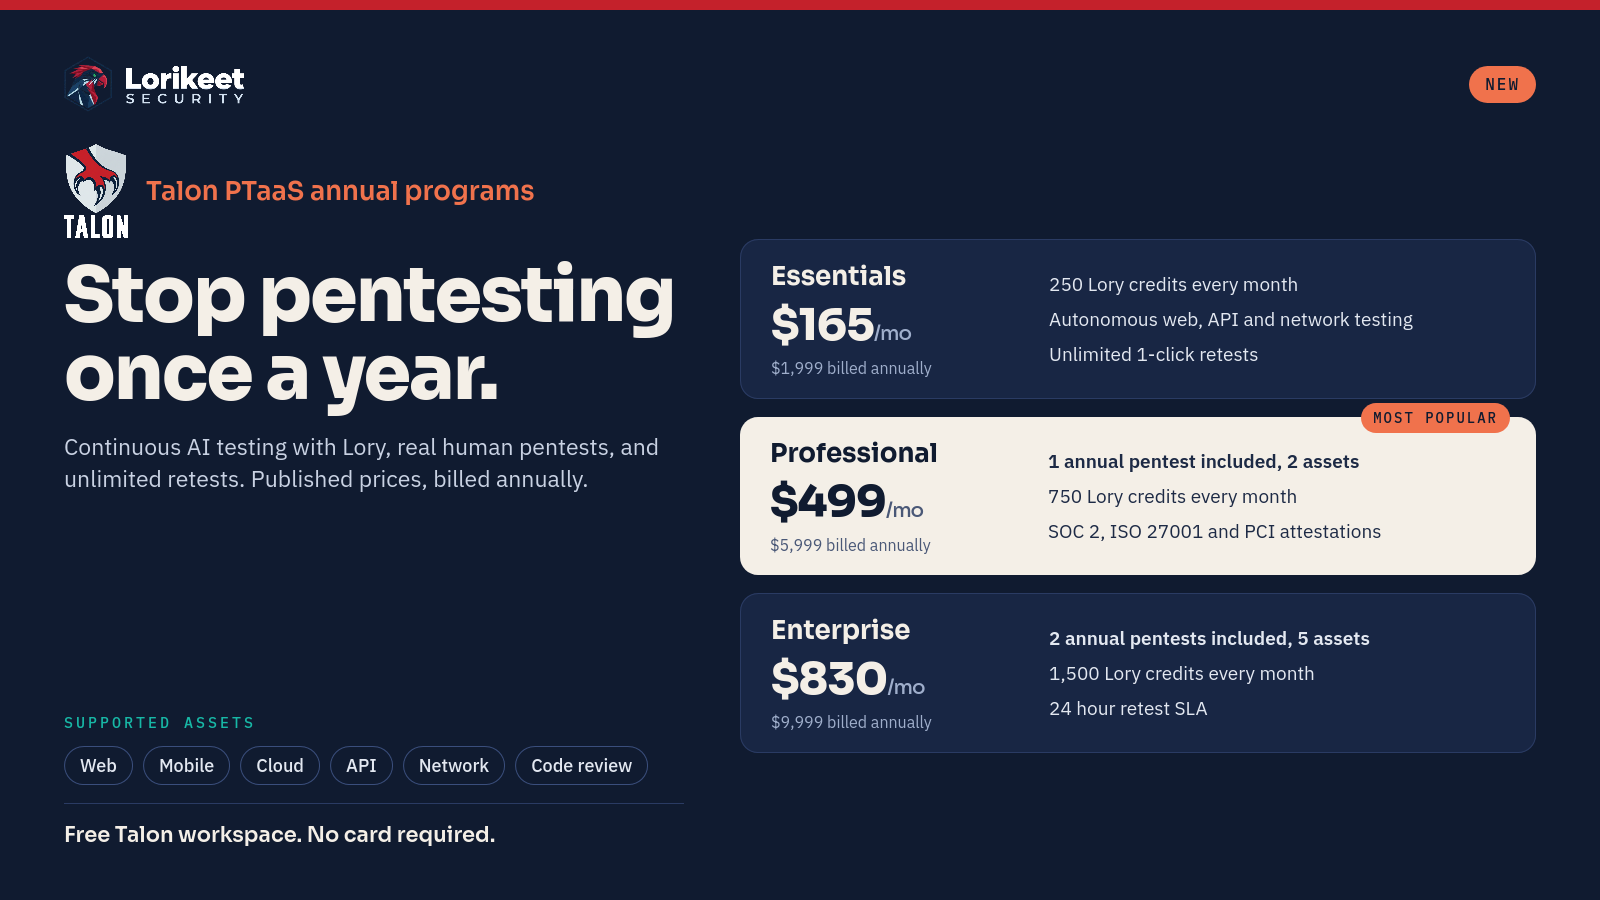
Lorikeet Security has revolutionized penetration testing across Florida with Talon PTaaS and its autonomous offensive validation engine, Lory AI. Designed specifically for modern engineering teams and compliance-driven businesses, Talon replaces obsolete once-a-year PDF reports with continuous attack surface coverage.
Key advantages for Florida businesses:
- Transparent Annual Subscriptions: Predictable pricing from $1,999 to $9,999/yr covering your entire estate: web applications, APIs, mobile apps (iOS/Android), multi-cloud/Kubernetes, internal networks & Active Directory, AI agents & LLMs, source code repos (VCS), and thick clients.
- 72-Hour Rapid Delivery: Testing begins immediately with confirmed findings streaming into your dashboard in real time.
- Unlimited 1-Click Retesting: Developers deploy a patch and request verification with a single click. Our certified human engineers re-verify the fix within 24 to 48 hours and update your compliance attestation letter for free.
- Talon MCP Server: Seamlessly synchronizes findings with developer IDEs like Cursor and Claude Code, generating automated patch diffs and pull requests.
- Florida Direct Support: Dedicated Florida engineering desk: (689) 202-3940.
2. Traditional National Consultancies
Established national consultancies like Crowe, Protiviti, and RSM operate regional offices throughout Florida. These firms are well-suited for organizations requiring bureaucratic procurement processes or physical on-site social engineering. However, their engagements carry substantial overhead: pricing typically starts at $15,000 to $30,000 per application, scheduling takes four to six weeks, and any code fix requires negotiating an additional retest change order.
3. Local Florida Regional IT & Managed Service Providers
Throughout Orlando, Tampa, and South Florida, hundreds of Managed Service Providers (MSPs) offer penetration testing on their line cards. In many cases, however, these providers do not employ full-time offensive red teamers; instead, they run an automated vulnerability scanner, export a white-labeled PDF, and charge a 400% markup. If your compliance auditor inspects the report, an automated scanner export will fail SOC 2 or PCI DSS attestation reviews.
Red Flag Warning: How to Spot "Fake" Pentest Firms in Florida
If a vendor promises a "comprehensive web application penetration test" for $1,500 and delivers the report in 2 hours, they ran an automated vulnerability scanner. True penetration testing requires certified human ethical hackers (OSCP, OSWE, GXPN, CREST) testing business logic flaws, race conditions, role-based access controls, and multi-step attack chains that no automated scanner can detect.
Penetration Testing Requirements by Florida Metro
Miami & South Florida (Brickell, Wynwood, Fort Lauderdale)
South Florida is dominated by fintechs, cross-border payment gateways, and wealth management platforms. The primary testing requirements focus on API security, Broken Object Level Authorization (BOLA), payment logic race conditions, and FIPA customer privacy protection.
Tampa Bay & St. Petersburg (Water Street, Westshore)
Tampa Bay represents a massive hub for healthcare systems, regional banking, and insurtech. Engagements here focus on HIPAA Security Rule attestation, electronic health record (EHR) integrations, PCI DSS 4.0 payment gateways, and SOC 2 Type II compliance.
Orlando & The I-4 Tech Corridor (Lake Nona, Space Coast)
Central Florida’s ecosystem is anchored by defense contractors, aerospace ventures, and healthtech. Key requirements include CMMC 2.0 Level 2 gap testing, NIST SP 800-171 controls, and cloud infrastructure IAM privilege escalation testing.
Jacksonville (Financial Services & Logistics)
Jacksonville’s corporate landscape centers on transportation, supply chain logistics, and banking. Pentesting focuses on cloud supply chain dependencies, web portal security, and external attack surface management (EASM).
Calculating ROI: Traditional Consulting vs. Talon PTaaS
According to Dr. Chenxi Wang’s landmark economic study on Penetration Testing as a Service, enterprise organizations utilizing continuous PTaaS realize 96% to 103% higher ROI than traditional consulting models. Traditional firms bill for administrative coordination, scoping SOWs, and manual PDF compilation. Talon PTaaS automates the operational friction, passing direct financial savings and internal engineering triage bandwidth back to your team.
Ready to Upgrade Your Florida Pentesting Program?
Join Florida technology leaders, healthcare providers, and defense contractors who rely on Talon PTaaS for auditor-accepted continuous validation and 72-hour report turnaround.