
Looking for Cacilian alternatives? As modern engineering teams accelerate deployment cycles and infrastructure becomes increasingly software-defined, traditional point-in-time penetration testing is being replaced by Penetration Testing as a Service (PTaaS). While Cacilian (developed by Prescient Security) has carved out a niche serving compliance-focused organizations, many security leaders and engineering teams find themselves evaluating alternatives that offer greater automation depth, modern AI-driven autonomous testing, native developer integrations, or enterprise-scale human testing.
This comprehensive comparison examines four leading PTaaS and offensive security platforms: Talon PTaaS (Lorikeet Security), Cacilian (Prescient Security), NetSPI PTaaS, and Bishop Fox Cosmos. We analyze their testing architectures, autonomous AI capabilities (including a head-to-head comparison of Lory AI vs. Cait AI), developer remediation workflows, compliance audit defensibility, and total cost of ownership (TCO).
Platform Overview: At a Glance
The PTaaS landscape in 2026 divides broadly into three distinct philosophies: compliance-driven portals (Cacilian), developer-first continuous offensive platforms (Talon PTaaS), and large-scale enterprise consulting engines (NetSPI and Bishop Fox). Here is how the four platforms compare at a high level:
| Platform | Core Philosophy | Key Differentiator | Best Suited For |
|---|---|---|---|
| Talon PTaaS (Lorikeet Security) | Continuous autonomous testing + certified human verification | Lory AI autonomous execution, native Talon MCP Server for Cursor/Claude Code, 100% transparent pricing ($165–$830/mo) | High-velocity SaaS, engineering-led security teams, startups to mid-market wanting continuous validation |
| Cacilian (Prescient Security) | Automated testing portal tied to compliance audit workflows | Deep GRC platform sync (Drata, Vanta), Cait™ AI testing, bundled compliance assessment options | SMBs focused primarily on rapid annual SOC 2/ISO compliance checklists |
| NetSPI PTaaS | Enterprise offensive security consulting at massive scale | 300+ in-house offensive engineers, 50+ specialized test lines (mainframe, IoT, medical) | Fortune 500 enterprises, tier-1 financial institutions, complex legacy hybrid environments |
| Bishop Fox Cosmos | Fully managed Continuous Threat Exposure Management (CTEM) | 2.3 billion operations/week, automated attack surface perimeter discovery with human triage | Fortune 100 technology enterprises with sprawling, dynamic external perimeters |
Cacilian (Prescient Security): Compliance-First PTaaS
Cacilian is the proprietary Penetration Testing as a Service platform developed by Prescient Security, a cybersecurity consulting and compliance advisory firm. Cacilian was built to eliminate the email-driven, spreadsheet-heavy workflows of legacy pentesting by giving clients a centralized web portal to scope engagements, monitor testing progress, review raw vulnerability feeds, and export compliance-ready PDF reports.
In recent releases, Prescient Security augmented Cacilian with Cait™ (Cacilian AI), an AI-assisted testing agent designed to crawl web applications, identify common vulnerabilities, and feed results back into the client portal.
Core Strengths of Cacilian
- Seamless GRC Platform Integration: Cacilian's strongest capability is its native pipeline into compliance automation platforms like Drata, Vanta, and Secureframe. When a test completes, attestations and executive summaries push directly into compliance evidence lockers.
- Unified Engagement Portal: Clients can initiate scoping, submit target URLs, schedule assessment windows, and view findings as they are logged rather than waiting for a delayed report delivery.
- Cait™ AI Assisted Scanning: Incorporates automated crawler routines to probe web application attack surfaces continuously between manual assessments.
- Audit-Focused Reporting: Reports generated through Cacilian are specifically tailored to satisfy auditor expectations for SOC 2 Type II, ISO 27001, HIPAA, and PCI DSS.
Limitations & Why Buyers Look for Alternatives
- Opaque, Quote-Based Pricing: Cacilian does not publish standard pricing tiers. Engagements require customized sales scoping calls, with annual costs typically scaling based on IP counts, user roles, and compliance packages—often ranging from $12,000 to $35,000+ per engagement.
- Lack of Modern Developer-Native Tooling: Cacilian relies on traditional CSV/PDF exports and basic ticketing webhooks. It lacks Model Context Protocol (MCP) server support, preventing developers from querying findings or triggering automated remediations directly inside modern AI IDEs like Cursor or Claude Code.
- Superficial AI Depth (Cait vs. Dedicated Reasoning Engines): Cait operates primarily as an enhanced automated web scanner rather than a multi-agent autonomous reasoning engine capable of complex multi-step chaining, zero-token Layer 3 recon, or authenticated privilege escalation across private subnets.
- Dependency on Traditional Consulting Overhead: Under the hood, scheduling, resourcing, and retesting turnaround remain subject to Prescient Security's consultant availability, meaning retests can incur scheduling friction or additional fees.
- Vendor Risk & Compliance Association: Some enterprise procurement teams remain cautious regarding Prescient Security's historical association with controversial compliance-tech engagements (such as the Delve SOC 2 audit scandal), preferring vendors with independent, unimpeachable offensive testing credentials.
Talon PTaaS (Lorikeet Security): Developer-First Continuous Security
Talon PTaaS by Lorikeet Security represents a generational shift in how penetration testing is delivered. Rather than treating pentesting as an annual compliance interruption, Talon embeds continuous offensive security directly into the modern developer workflow. Talon combines autonomous AI penetration testing via Lory AI with mandatory, certified Human-in-the-Loop offensive security verification by senior OSCP, OSCE, and CISSP engineers.
How Talon PTaaS Works
- Autonomous Execution with Lory AI: Lory autonomously maps external perimeters, crawls modern single-page applications (SPAs) with headless Chromium, audits REST and GraphQL APIs for BOLA/IDOR, and probes cloud IAM boundaries using continuous agentic reasoning.
- Zero-False-Positive Human Sign-Off: Pure AI scanners overwhelm developers with false positives. Talon enforces a strict mandate: every critical, high, and medium severity vulnerability discovered by Lory must be verified, reproduced, and countersigned by a human OSCP/CISSP engineer before alerting engineering.
- Native Talon MCP Server (Cursor & Claude Code): Talon is the first PTaaS platform with an official Model Context Protocol server. Developers can ask their AI coding assistant to explain a Talon vulnerability, view verified reproduction curl scripts, apply remediation code diffs, and invoke 1-click retest validation directly from their IDE.
- Zero-Trust Private Subnet Connector: Test internal staging environments, private microservices, and AWS/GCP VPCs safely without opening inbound firewall ports, whitelisting static IPs, or configuring brittle VPN tunnels.
- Unlimited 1-Click Retesting: Whenever your engineers patch a flaw, click "Retest" in Talon or trigger it via API. Lory re-executes the exact exploit payload and confirms remediation within minutes at zero extra charge.
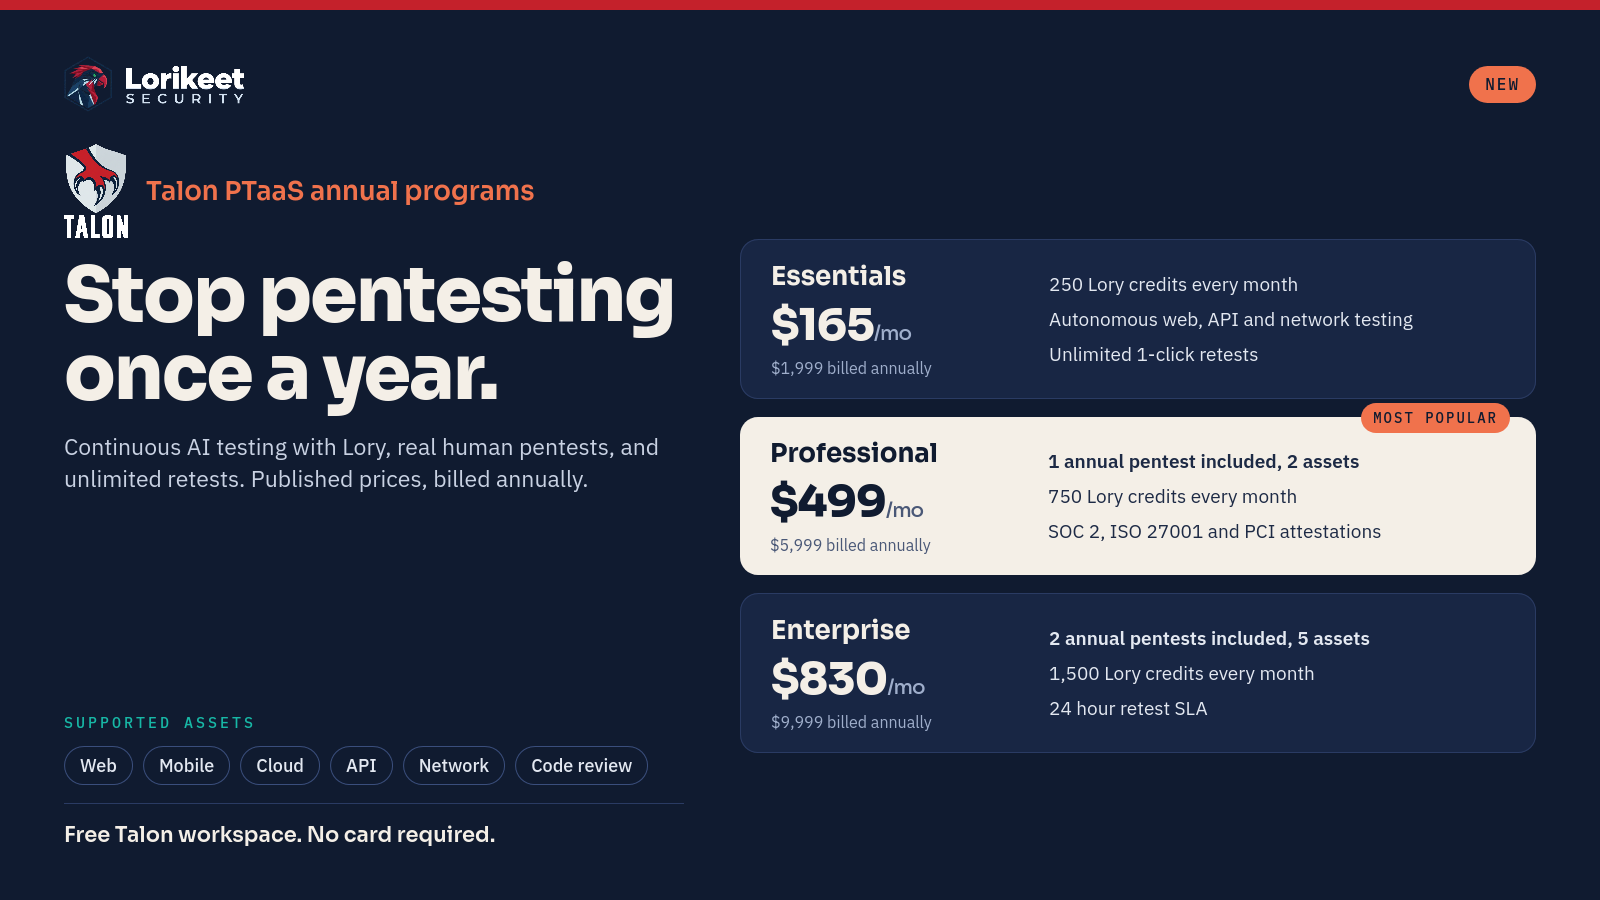
- Transparent, Self-Serve Pricing: Unlike legacy PTaaS vendors that hide behind sales walls, Talon publishes all subscription plans publicly—starting at $165/month for Essentials and $499/month for Professional with formal audit attestations included.
Talon PTaaS Annual Subscription Tiers
| Tier | Annual Rate | Included Coverage | Key Features |
|---|---|---|---|
| Talon Free Workspace | $0 / month | Pay-as-you-go Lory credits ($25+) | Findings dossier, report viewer, Talon MCP Server, pay-as-you-go autonomous sweeps |
| Talon Essentials | $165 / mo ($1,980/yr) | 1 Web App / Perimeter + Monthly Lory sweeps | Continuous external perimeter monitoring, monthly scheduled Lory tests, Jira/GitHub sync, Talon MCP Server, 1 annual human pentest attestation |
| Talon Professional (Most Popular) | $499 / mo ($5,988/yr) | 3 Web Apps / APIs + Weekly Lory sweeps + Private Subnet | Private Subnet Connector, continuous API/cloud audits, weekly deep sweeps, unlimited 1-click retests, 2 formal human-verified SOC 2 / ISO audit reports |
| Talon Enterprise | $830 / mo ($9,960/yr) | Full multi-VPC attack surface + Continuous sweeps | Multi-region VPC mesh, custom attack trees, dedicated offensive engineer, continuous auditor attestations, bespoke compliance dossiers |
AI Pentesting Head-to-Head: Lory AI vs. Cait AI
Both Lorikeet Security and Cacilian advertise artificial intelligence capabilities within their PTaaS offerings. However, their underlying architectures, autonomy levels, and execution isolation differ significantly:
| Dimension | Lory AI (Talon PTaaS) | Cait™ AI (Cacilian) |
|---|---|---|
| Underlying Engine | Multi-agent autonomous offensive reasoning engine with Layer 3 zero-token deterministic recon | Automated web application crawler with LLM-assisted vulnerability matching |
| Authentication & Sessions | Multi-role authenticated stateful testing; tests BOLA/IDOR by swapping session tokens across privilege levels | Standard authenticated crawling; primarily checks for injection and known CVE signatures |
| Single-Page App (SPA) Handling | Headless Chromium crawler renders dynamic React, Vue, Angular DOM states and client-side routes | Standard HTTP client crawler; limited dynamic client-side DOM interaction |
| Credential Security | Zero-knowledge vault: AES-256-GCM encryption, prompt token masking, ephemeral memory zeroing | Standard portal credential storage |
| Human Verification | Mandatory OSCP & CISSP countersignature on all findings before developer alerts | Automated findings published directly to portal, reviewed during manual phases |
| IDE Integration | Native Talon MCP Server for real-time query and auto-fix in Cursor and Claude Code | No IDE integration (web portal & webhook exports only) |
| Retesting Velocity | Autonomous 1-click retest; confirms code patches in minutes | Retesting scheduled through portal or queued for next assessment cycle |
NetSPI PTaaS: Enterprise Breadth at Massive Scale
NetSPI is one of the most established names in penetration testing, pioneering the enterprise PTaaS model over two decades ago. With more than 300 in-house certified testers, NetSPI has evaluated over 4 million assets and serves 9 of the top 10 U.S. banks, major cloud service providers, and Fortune 500 multinationals.
Platform Strengths
- Unrivaled Depth of Specialized Testing: Offers over 50 distinct penetration testing services, including rare enterprise specialties such as IBM z/OS mainframe testing, automotive CAN bus security, medical devices, and ATM hardware assessments.
- High-Touch Enterprise Account Management: Enterprise clients receive dedicated Client Delivery Managers, bespoke scoping meetings, and tailored executive presentations.
- Hybrid Testing Methodology: Combines proprietary automation tooling with rigorous manual penetration testing methodologies aligned with NIST SP 800-115 and OWASP.
Trade-Offs & Considerations
- High Minimum Financial Commitment: NetSPI is engineered for large enterprise budgets. Annual commitments typically exceed $25,000 to $100,000+, making it economically impractical for early-stage startups and mid-market engineering teams.
- A La Carte Retesting Fees: Depending on contract tier, fix verification and retesting can incur additional hourly charges or require separate retest credits.
- Consultant-Heavy Turnaround: Because testing relies heavily on human scheduling blocks, rapid daily/weekly validation for fast-shipping continuous delivery pipelines can encounter scheduling latency.
Bishop Fox Cosmos: Continuous External Perimeter Defense
Bishop Fox is universally respected as an offensive security powerhouse. Its flagship PTaaS product, Cosmos, focuses on Continuous Threat Exposure Management (CTEM). Cosmos executes over 2.3 billion automated and manual security operations weekly across client perimeters, designed specifically to identify shadow IT, forgotten subdomains, and exposed cloud services.
Platform Strengths
- Relentless External Attack Surface Discovery: Cosmos shines at mapping vast, sprawling corporate perimeters, uncovering unknown subdomains, open cloud storage buckets, and unpatched perimeter services before attackers do.
- Expert-Validated Telemetry: Automated findings undergo validation by Bishop Fox operators to suppress false alarms before notifications reach client security teams.
- Unlimited Fix Verification: Fix validation is bundled into the continuous service, allowing clients to re-verify perimeter exposures without additional fees.
Trade-Offs & Considerations
- Perimeter Focus vs. Deep Authenticated Logic: Cosmos is primarily an external attack surface and threat exposure platform. While they offer Application Pentesting as a separate service, continuous automated coverage does not delve as deeply into authenticated business logic, multi-role IDOR, or private staging VPCs as dedicated PTaaS platforms.
- Enterprise-Only Pricing: Cosmos requires custom scoping and annual enterprise contracts, generally starting around $35,000 to $120,000+ depending on IP counts and perimeter complexity.
- No Direct Developer IDE Integration: Lacks Model Context Protocol integration, relying instead on Jira/Slack notifications and portal dashboards.
Comprehensive Feature Comparison Matrix (2026)
| Feature / Capability | Talon PTaaS (Lorikeet Security) | Cacilian (Prescient Security) | NetSPI PTaaS | Bishop Fox Cosmos |
|---|---|---|---|---|
| Testing Model | Continuous Autonomous + Certified Human-in-the-Loop | Continuous Portal + Scheduled Human Testing | Hybrid Automated + In-House Manual Pentesting | Fully Managed Continuous Attack Surface (CTEM) |
| Autonomous AI Engine | Lory AI (Multi-Agent Reasoning, Headless SPA Crawler) | Cait™ AI (Web Scanner) | Proprietary DAST/Automation Scripts | Automated Perimeter Scanners (2.3B ops/wk) |
| Human Verification | Mandatory 100% (OSCP/CISSP countersigned) | Included in scheduled tests; raw AI alerts in portal | 100% verified by 300+ in-house staff | Human analyst triage on exposure alerts |
| Developer IDE Integration | Talon MCP Server (Cursor & Claude Code native) | None (Webhooks only) | None (Ticketing integration only) | None (Jira / SIEM only) |
| Private Subnet Testing | Zero-Trust Connector (No inbound ports or VPNs) | Requires VPN / IP whitelisting | Dedicated jumpbox / VPN connection | Limited (Perimeter focus) |
| Authenticated BOLA/IDOR Audits | Autonomous multi-role token swapping | Manual pentest phase only | Manual pentest phase | Separate application testing engagement |
| GRC Platform Sync | Drata, Vanta, Secureframe, Tugboat Logic | Drata, Vanta, Secureframe | Custom GRC connectors | Jira, ServiceNow, custom API |
| 1-Click Retesting | Unlimited & instant on all annual plans | Portal request; subject to scheduling | A la carte / contract dependent | Unlimited perimeter fix verification |
| Published Pricing | 100% Public ($165–$830/month) | Opaque (Contact sales) | Opaque (Contact sales) | Opaque (Contact sales) |
| Starting Annual Cost | $1,980 / year (or $0 free workspace) | ~$12,000+ / year | ~$25,000+ / year | ~$35,000+ / year |
| Audit Attestation Included | Yes (SOC 2, ISO 27001, PCI on Pro & Enterprise) | Yes (Formal compliance reports) | Yes (Enterprise attestations) | Yes (Perimeter posture letters) |
Pricing and Total Cost of Ownership (TCO)
One of the primary frustrations security and engineering leaders express with legacy PTaaS vendors is pricing opacity. Traditional consulting and first-generation PTaaS platforms force buyers through multi-week sales cycles, scope negotiations, and variable billable hours for retesting. Here is how annual costs and TCO compare across typical use cases:
| Scenario | Talon PTaaS | Cacilian | NetSPI | Bishop Fox Cosmos |
|---|---|---|---|---|
| Seed / Series A SaaS (1 Web App, 1 API, Annual SOC 2) | $1,980 – $5,988/yr (Talon Essentials or Pro; includes audit report + retests) | $12,000 – $18,000/yr (Single scoped test + compliance package) | $25,000+/yr (Exceeds minimum engagement size) | $35,000+/yr (Overkill for simple single-asset perimeter) |
| Growth-Stage SaaS (3 Apps, Staging VPC, Continuous SOC 2 & ISO) | $5,988/yr (Talon Professional; includes Zero-Trust Connector + 2 audit reports) | $22,000 – $35,000/yr (Multi-asset scoping + manual retest fees) | $45,000 – $75,000/yr (Comprehensive multi-target engagement) | $50,000 – $80,000/yr (Continuous CTEM + manual app tests) |
| Enterprise / Multi-Cloud (Sprawling perimeter, Multi-VPC, Custom compliance) | $9,960/yr (Talon Enterprise; continuous mesh coverage + dedicated engineer) | $40,000 – $70,000+/yr (Enterprise custom quote) | $80,000 – $150,000+/yr (Full enterprise programmatic PTaaS) | $90,000 – $160,000+/yr (Enterprise Cosmos CTEM license) |
The TCO Takeaway: By combining autonomous Lory AI execution with streamlined certified human countersignatures, Talon PTaaS achieves a 60% to 80% reduction in total offensive security spend while dramatically increasing testing frequency from once a year to continuous weekly and real-time coverage.
Which Platform Is Right for Your Team?
Choose Talon PTaaS (Lorikeet Security) If:
- You want continuous offensive coverage instead of an annual static snapshot that expires the moment code is deployed.
- Your developers use modern AI coding assistants (Cursor, Claude Code) and would benefit from Talon's native MCP Server to reproduce and fix vulnerabilities in seconds.
- You need to test private VPCs, staging clusters, or internal APIs without punching holes in firewalls using the Zero-Trust Private Subnet Connector.
- You refuse to pay unpredictable hourly billing for fix verification and demand unlimited, instant 1-click retesting.
- You value transparent, published pricing with flexible self-serve subscriptions ($165 to $830/month) backed by senior OSCP/CISSP audit attestations.
Choose Cacilian (Prescient Security) If:
- Your primary motivation is satisfying a basic GRC checklist (Drata, Vanta) for an upcoming audit and you already work with Prescient Security's advisory team.
- You prefer an automated, portal-driven engagement rather than legacy PDF email chains, and require minimal internal engineering interaction during testing.
Choose NetSPI If:
- You represent a Fortune 500 bank, major healthcare provider, or tier-1 enterprise requiring 50+ specialized test lines—including legacy IBM z/OS mainframes, ATM firmware, or medical telemetry devices.
- You have an established six-figure security testing budget and require dedicated high-touch client delivery managers.
Choose Bishop Fox Cosmos If:
- Your primary security vulnerability is an uncontrollable, sprawling external digital footprint with hundreds of forgotten domains and shadow IT cloud assets.
- You want an always-on, fully managed perimeter threat exposure service backed by one of the most celebrated offensive research teams in cybersecurity.
Conclusion: The Future of PTaaS Is Continuous and Developer-First
While Cacilian represented an important first step away from traditional manual consulting toward portal-based PTaaS, modern engineering teams require more than just an automated dashboard. Today's high-velocity deployment cadences demand autonomous offensive depth, zero-friction developer integration via MCP, and guaranteed zero-false-positive human verification.
By pairing Lory AI with certified OSCP & CISSP engineers, Talon PTaaS delivers the rigor of enterprise penetration testing at the speed of modern software development—with transparent pricing that puts continuous offensive security within reach of every growth-stage organization.
Explore Next Steps
| Platform | Key Strength | Learn More |
|---|---|---|
| Talon PTaaS | Continuous autonomous testing, Lory AI, Talon MCP Server, transparent plans | Explore Talon PTaaS | View Pricing |
| Lory AI | Autonomous multi-agent penetration testing engine with human verification | Discover Lory AI |
| Cacilian | Prescient Security's automated compliance PTaaS portal | cacilian.com |
| NetSPI | Enterprise PTaaS at scale with 300+ certified specialists | netspi.com |
| Bishop Fox Cosmos | Continuous Threat Exposure Management (CTEM) for sprawling perimeters | bishopfox.com/cosmos |

