
Meet Lory: Autonomous Pentesting by the Credit — Plans, Economics, and Architecture
The economics of software vulnerability testing have been fundamentally broken for over a decade. Engineering organizations deploy code continuously, yet they test offensively once every twelve months because hiring human penetration testers for every minor release is cost-prohibitive. On the other end of the spectrum, automated vulnerability scanners flood engineering queues with hundreds of unverified alerts and false positives.
Enter Lory: Lorikeet Security’s autonomous AI penetration testing agent. Built specifically for modern offensive operations, Lory performs scoped, intelligent exploitation against web applications, APIs, cloud environments, mobile apps, and internal network infrastructure.
Unlike legacy software that charges rigid annual per-seat licenses, Lory is priced transparently by the credit. There are no punitive user limits, no "use-it-or-lose-it" expirations, and no surprise charges: $1 buys exactly 1 credit. Lory draws down credits as she works, giving engineering teams complete control over their offensive security spend.
The Golden Rule of Lory: Credits never expire. Unused credits from any monthly plan automatically roll forward into subsequent months. You can also fund testing on-demand with pay-as-you-go credits starting at just $25 with no active monthly subscription.
How the Lory Credit Model Works
Lory's billing architecture directly mirrors the compute and intelligence resources consumed during an offensive engagement. Every action is metered through three transparent line items:
| Resource Key | Billing Unit | Cost in Credits | What You Are Buying |
|---|---|---|---|
| MCP RPC Call | Per call | 0.10 credit | Every tool call made through Model Context Protocol (MCP) tokens: vulnerability lookups, scope verification, and knowledge base retrievals. |
| Engine Tokens | Per 1,000 tokens | 0.02 credit | Input and output reasoning tokens consumed by Lory while dissecting application logic, constructing payloads, and bypassing defenses. |
| Scanner Compute | Per minute | 0.10 credit | Wall-clock compute in the sandboxed toolbelt: headless browser crawls, port enumeration, Nuclei template execution, and fingerprinting. |
Engagement Depths & Deterministic Budget Ceilings
When scoping an engagement against an asset (e.g., your staging environment, a GraphQL endpoint, or an AWS IAM configuration), you select an Engagement Depth. Each depth enforces strict token and wall-clock compute budgets so Lory never runs away with unexpected expenses.
Engagements finish when the vector plan is satisfied, meaning typical engagements cost significantly less than the worst-case budget ceiling:
| Engagement Depth | Scope & Methodology | Budget Ceilings (Hard Limit) | Typical Engagement Cost |
|---|---|---|---|
| Surface (Weight 1.0) | Perimeter reconnaissance, port scans, DNS & subdomain enumeration, exposed secrets, and obvious web attack surface. | 2.5M tokens · 70 min compute Max Ceiling: $57.00 |
~$19 – $25 |
| Standard (Weight 1.5) | Full OWASP Top 10 vector plan, authentication flows, session handling, IDOR / BOLA analysis, input fuzzing, and API validation. | 6.5M tokens · 183 min compute Max Ceiling: $215.00 |
~$70 – $95 |
| Deep (Weight 2.5) | Exhaustive multi-step chained exploitation, out-of-band payloads, complex business logic flaws, and long-running security tooling. | 24.0M tokens · 12 hrs compute Max Ceiling: $1,380.00 |
~$450 – $580 |
Monthly Credit Subscription Plans
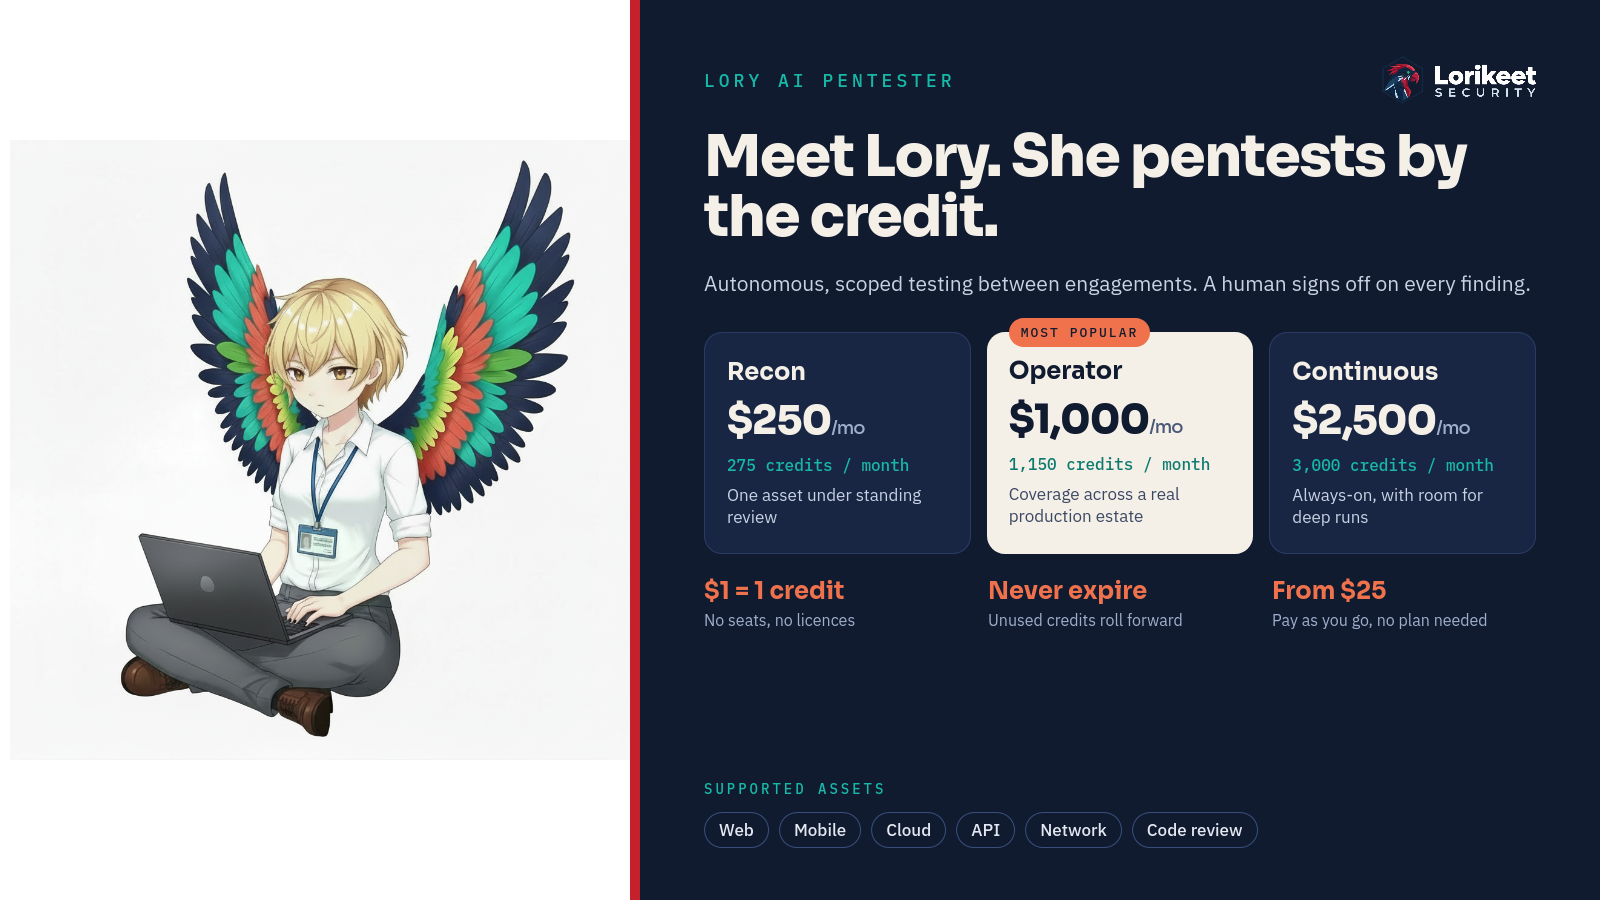
While pay-as-you-go allows any team to get started for $25, monthly subscription plans provide significant credit bonus discounts. Subscribing ensures your attack surface is defended with regular standing sweeps and continuous coverage between major releases:
Recon
One asset kept under standing weekly review
- 275 credits added every month
- 1 to 3 Standard assessments, or ~13 Surface sweeps
- Unused credits roll forward indefinitely
- Web, API & cloud perimeter scanning
- Real-time finding dashboard
- Standard support
Operator
Continuous coverage across a production estate
- 1,150 credits added every month
- 5 to 14 Standard assessments
- Headroom for Claude Code / Cursor MCP traffic
- Unused credits roll forward indefinitely
- Full multi-asset scoped coverage
- Priority queue processing
Continuous
Always-on testing with deep-depth headroom
- 3,000 credits added every month
- 2 to 6 Deep chained assessments, or ~37 Standard
- High-volume MCP agent integration
- Private VPC testing via Lory Mesh
- Unused credits roll forward indefinitely
- Priority engineer triage SLA
The Critical Differentiator: Certified Human Countersignatures
In the cybersecurity market, unverified AI scanners are notorious for generating noise. When an AI tool claims an application is vulnerable to SQL injection simply because an error message contains a single quote, developers waste hours investigating non-issues.
Lorikeet solves this through our Human-in-the-Loop (HITL) Verification Protocol:
- Autonomous Execution: Lory executes attack playbooks, probes parameters, and attempts safe proof-of-concept exploits.
- PoC Capture: When Lory believes she has uncovered a flaw, she compiles a structured dossier including exact HTTP requests, headers, payload bodies, and system responses.
- Certified Analyst Countersignature: Before the finding appears in your Talon dashboard or sends a webhook notification, a certified Lorikeet offensive security engineer (OSCP/CREST) manually reviews the evidence. If it is a false positive, it is discarded immediately. If valid, the engineer verifies the severity rating and confirms the remediation advice.
Zero False Positives: When your developers see a notification from Lory, they know it has been confirmed by a human offensive security specialist. You never waste sprint capacity triaging AI hallucinations.
Comprehensive Multi-Asset Coverage
Lory isn't restricted to basic web pages. Her testing engine spans five critical enterprise asset classes:
Whether you need to test an OAuth 2.0 implementation with token refresh edge cases, assess whether an S3 bucket is leaking sensitive customer documents, or test an internal microservice behind a private WireGuard VPN, Lory has specialized vector modules ready to deploy.
Buyer Decision Checklist: Estimating Your Monthly Credit Consumption
Use this simple rule of thumb to estimate your team's monthly credit requirements:
- Single Web Application (Weekly Sprints): 1 Surface sweep per week (~80 credits) + 1 Standard engagement per month (~85 credits) = ~165 credits/month → Recon Plan ($250/mo) leaves 110 credits rolling forward monthly.
- Two Applications + API Gateway: 2 Standard engagements per month (~170 credits) + 8 Surface sweeps (~160 credits) + MCP developer queries (~50 credits) = ~380 credits/month → Operator Plan ($1,000/mo) provides ample headroom.
- Enterprise Platform with Multi-Tenant Architecture: Weekly continuous sweeps across 10+ subdomains, monthly deep tests against core services, and heavy developer MCP usage = 1,800 to 2,600 credits/month → Continuous Plan ($2,500/mo).
Deploy Your First Autonomous Pentest Today
Experience the precision of autonomous AI testing backed by human security engineers. Launch your free workspace, top up as little as $25, and inspect your attack surface within minutes.


