
Talon PTaaS Pricing Guide 2026: Continuous Pentesting Plans, TCO, and Buyer ROI
In 2026, security and engineering leaders are facing an acute budgeting reality: software delivery has accelerated to hourly production deploys, while traditional penetration testing costs remain exorbitant, opaque, and trapped in an archaic waterfall framework.
A standard legacy consulting firm charges anywhere between $25,000 and $60,000 for a single annual penetration test against two or three core assets. Six weeks later, you receive a static 70-page PDF report. If your developers ship a remediation patch the following week, verifying the fix requires negotiating a change order or paying an additional $2,500 to $5,000 "retesting fee."
Most dangerously of all, that annual test leaves 364 days of complete offensive blind spots.
This economic and operational breakdown explains why high-velocity SaaS teams, healthcare technology innovators, and fintech platforms are migrating to Penetration Testing as a Service (PTaaS). In this comprehensive buyer guide, we provide an unvarnished breakdown of Talon PTaaS pricing, evaluate the Total Cost of Ownership (TCO) compared to legacy consulting, and explain how continuous validation unblocks audit compliance in record time.
Talon PTaaS Annual Plans: Full Breakdown
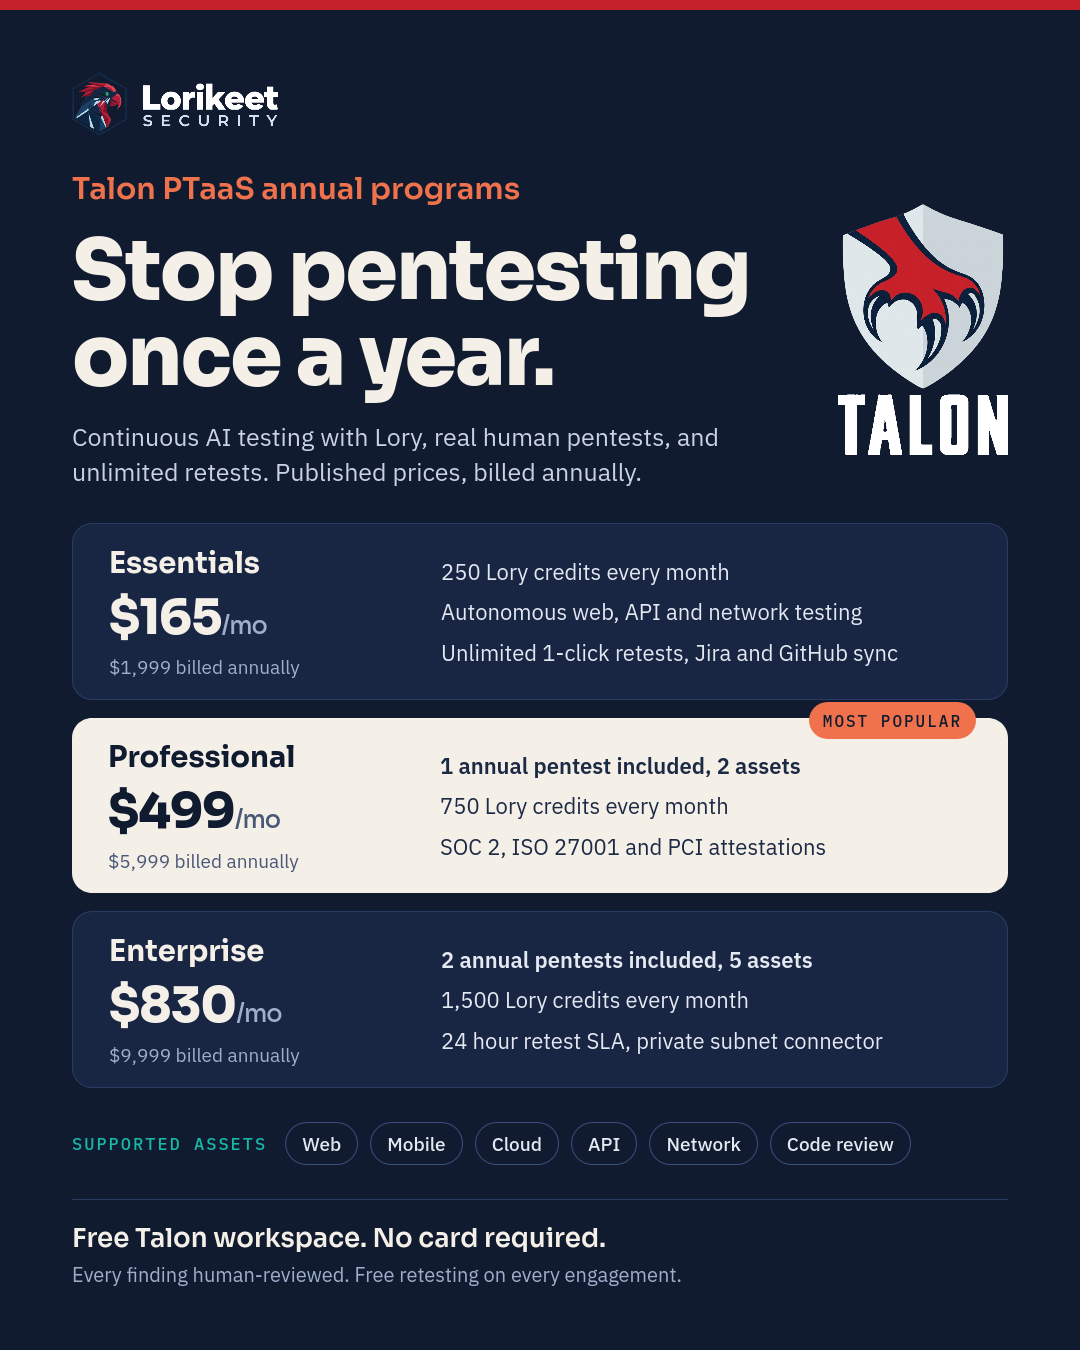
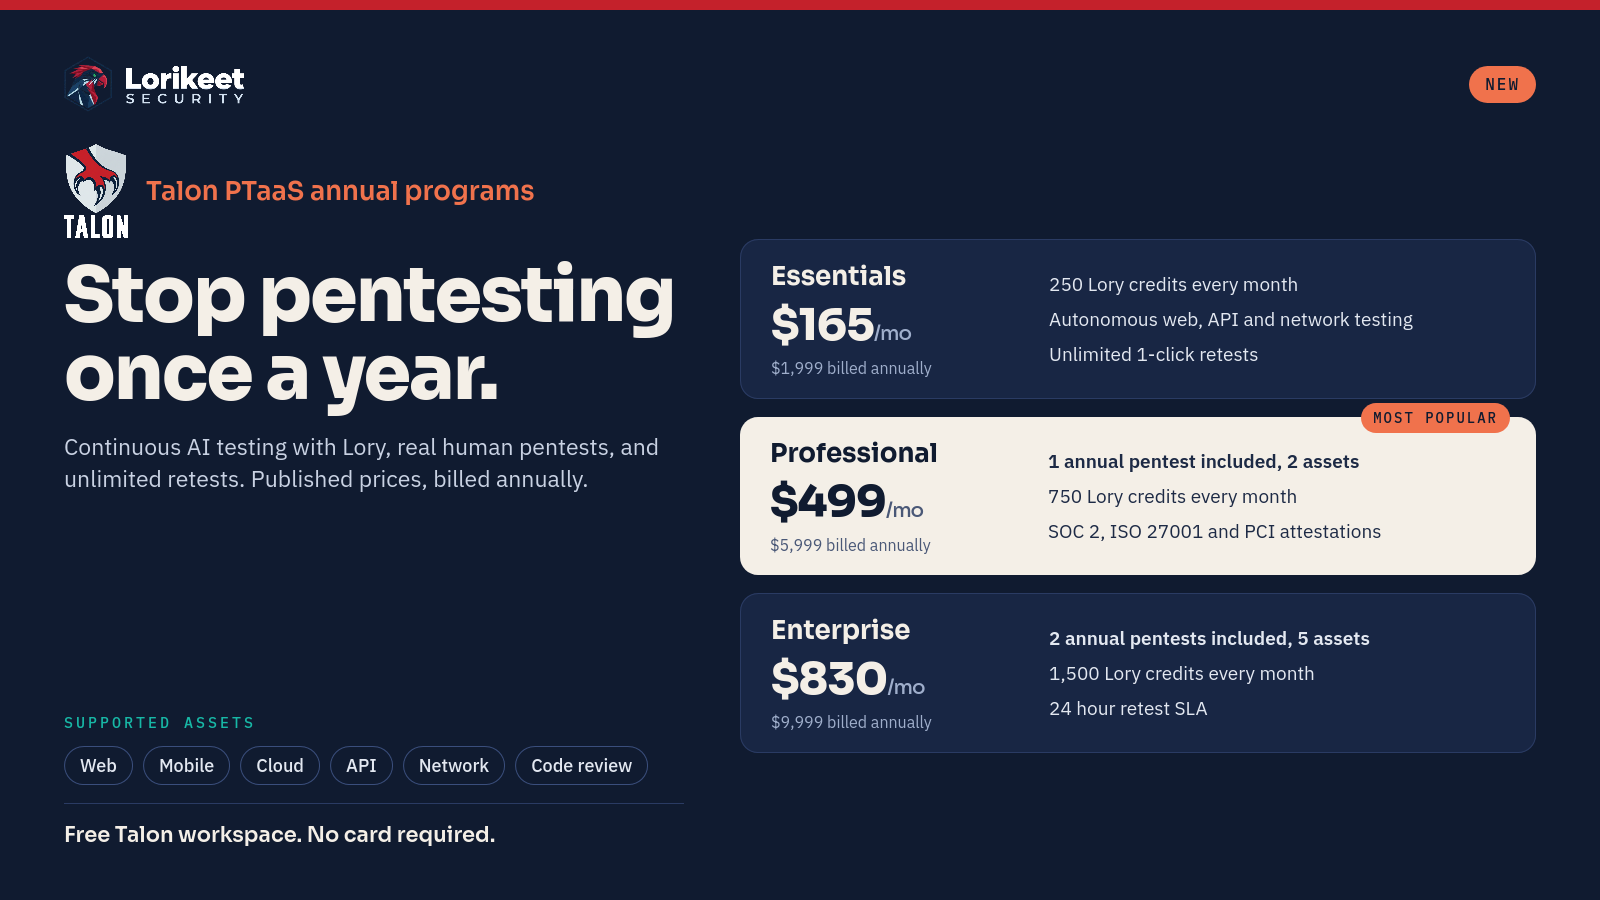
The Talon Platform was engineered around a simple premise: offensive security should be continuous, transparently priced, and seamlessly embedded into the developer loop. Rather than charging unpredictable hourly consulting rates, Talon bundles scheduled human penetration testing with continuous autonomous offensive coverage via Lory AI into predictable annual subscriptions.
Essentials
Continuous autonomous testing for fast-shipping teams
- 250 Lory Credits/Mo Included
- Autonomous Web, API & Network testing
- Real-time finding dossiers & PoC repros
- Unlimited 1-click retest verifications
- Talon MCP Server (Cursor & Claude Code)
- Bi-directional Jira & GitHub Sync
- SOC 2 & ISO 27001 readiness summaries
- Standard email & ticket support
Professional
Annual pentest paired with continuous AI coverage
- 1x Annual Pentest Included (2 Assets)
- Web App, API & Cloud Infrastructure
- 750 Lory Credits/Mo Included
- Autonomous AI testing between engagements
- Unlimited 1-click retest verifications
- Auditor-ready SOC 2, ISO & PCI attestations
- Talon MCP Server & IDE integration
- Dedicated Lead Security Engineer
- Shared Slack or MS Teams channel
Enterprise
Multi-target continuous offensive coverage & SLAs
- 2x Annual Pentests Included (5 Assets)
- Web, Mobile, Cloud, API & Code Review
- 1,500 Lory Credits/Mo Included
- Continuous autonomous offensive operations
- Lory Mesh private subnet connector
- Priority 24-hour retest verification SLA
- Multi-framework attestations (HIPAA, SOC 2, PCI)
- Hands-on remediation advisory
- Dedicated Lead Security Advisor
Talon Free Workspace ($0/month): Every organization starts with free access to the Talon Workspace. You can access past penetration test reports, export vulnerability findings dossiers, and connect your IDEs via the Talon MCP Server. Autonomous testing with Lory AI can be launched on-demand with pay-as-you-go credits starting at just $25 with no upfront contract.
Total Cost of Ownership (TCO): Traditional Pentest vs. Talon PTaaS
When calculating the true financial impact of security testing, procurement teams often look only at the line-item invoice for the test itself. However, the Total Cost of Ownership (TCO) includes four hidden expense drivers that inflate traditional consulting engagements:
- The Retest Tax: Traditional firms charge between $1,500 and $5,000 to verify that remediations are effective. If a team requires two retest rounds across a complex application, testing fees jump by 30% to 50%.
- Engineering Triage Overhead: Parsing a 70-page static PDF requires security engineers or engineering managers to spend 15 to 25 hours manually transcribing findings into Jira tickets, assigning severities, and clarifying ambiguous reproduction steps.
- Deal Slippage and Delayed Sales Cycles: When enterprise buyers demand an updated pentest report or SOC 2 attestation letter before closing, waiting 4 to 6 weeks for a consulting slot delays ARR recognition and damages enterprise sales velocity.
- Interim Exposure Costs: Finding a vulnerability during month 11 of an annual cycle means that flaw was potentially exploitable in your production environment for nearly a full year.
| Cost & Operational Dimension | Traditional Pentest Firm (Annual) | Talon PTaaS Professional | Annual TCO Impact |
|---|---|---|---|
| Initial Assessment Base Fee | $18,000 – $35,000 (2 assets) | $5,999 / year (includes 2 assets) | Save $12,000 – $29,000 |
| Remediation Retesting Fees | $2,500 – $5,000 per cycle | $0 (Unlimited 1-click retests) | Save $2,500 – $5,000 |
| Continuous Coverage (Between Audits) | $0 (Zero coverage; 364-day blind spot) | 750 Lory Credits/mo included | Continuous autonomous testing |
| Developer Workflow Integration | Manual PDF copy-paste into Jira | Native MCP IDE sync + 2-way Jira/GitHub | Saves 40+ engineering hours |
| Auditor Attestation Delivery | 3 – 4 weeks post-retest | Instant 72-hour verified attestation | Eliminates procurement delays |
| Total Estimated Annual TCO | $28,500 – $52,000 | $5,999 | 78% Total Cost Savings |
Why Traditional 364-Day Blind Spots Fail Modern Compliance
Compliance frameworks like SOC 2 Type II, ISO/IEC 27001:2022, and PCI DSS v4.0 have evolved dramatically. In previous years, presenting an annual PDF pentest report from any accredited firm was sufficient to check the box for auditor control CC7.1 or Annex A 8.8.
Today, enterprise auditors ask a fundamentally different question: "How do you ensure security controls remain operational across weekly software releases?"
If you push code to production 40 times a month, a point-in-time test conducted in March tells the auditor nothing about the security posture of an API endpoint deployed in August. Talon PTaaS closes this gap:
- Standing Lory AI Engagements: Autonomous offensive agents continuously sweep attack surfaces, test authentication mechanisms, and assess API endpoints as new pull requests are merged.
- Human Lead Sign-Off: Every finding produced by autonomous testing is reviewed and verified by Lorikeet’s human offensive security engineers, preventing hallucinated vulnerabilities or false alarm tickets.
- Live Auditor Portals: Rather than circulating sensitive PDFs over unencrypted email, compliance managers can generate secure, read-only auditor verification links with time-bounded access.
Buyer Decision Checklist: Which Talon Plan Fits Your Needs?
Selecting the right PTaaS plan depends on your team's funding stage, compliance timeline, and deployment velocity. Use this quick decision matrix to identify your optimal tier:
Choose Talon Essentials ($165/mo) if:
- You are an early-stage startup (pre-seed or seed) with continuous deployments but no formal external human pentest requirement yet.
- Your engineering team wants an autonomous security guardrail integrated directly into Claude Code or Cursor via Talon's MCP server.
- You need a centralized vulnerability tracking platform with automated GitHub and Jira issue resolution.
Choose Talon Professional ($499/mo) if:
- You have an immediate enterprise sales deal or SOC 2 Type II / ISO 27001 audit requiring a certified third-party pentest report.
- You maintain up to two primary assets (e.g., a customer-facing web application and its backend REST/GraphQL API).
- You want continuous autonomous offensive coverage between annual human assessments to ensure no regression vulnerabilities slip through.
- You value having a direct Slack or Teams connection to a named Lead Security Engineer.
Choose Talon Enterprise ($830/mo) if:
- You manage multiple products or complex environments spanning web apps, iOS/Android mobile apps, cloud infrastructure, and internal networks.
- You require private subnet testing behind VPCs via Lory Mesh WireGuard tunnels.
- Your enterprise compliance mandates strict 24-hour SLA verification on critical patch retests.
- You need executive presentations, quarterly attack surface reviews, and formal risk advisory for board-level reporting.
Ready to Modernize Your Pentest Program?
Stop burning budget on one-off PDF reports. Get transparent pricing tailored to your exact tech stack in under 60 seconds with our interactive calculator, or speak directly with our offensive security team.


