
Over the last five years, Miami has transformed from a vibrant tourist capital into one of the most dynamic technology and financial ecosystems in the Americas. Anchored by the banking towers of Brickell Avenue, the startup accelerators of Wynwood, and an influx of international capital from Latin America and New York, South Florida is home to a surging concentration of cross-border payment platforms, real estate tech startups, digital banking portals, and decentralized finance protocols.
However, this rapid growth brings elevated adversarial attention. Financial platforms moving billions across borders and consumer apps scaling at breakneck speed represent prime targets for cybercrime syndicates and automated vulnerability bots. In this environment, relying on annual static vulnerability scans is an invitation to catastrophe. Web application penetration testing has become a non-negotiable requirement for Miami companies seeking enterprise contracts, institutional banking licenses, and regulatory compliance.
The South Florida Risk Profile: Why Miami Apps Face Unique Threats
Miami’s corporate and technological landscape introduces distinct cybersecurity challenges:
1. Cross-Border Financial Architectures (LatAm Gateway)
Many Miami fintechs operate dual-currency architectures, foreign exchange (FX) rails, and multi-jurisdictional APIs integrating US banking networks (FedNow, ACH) with Latin American systems (such as Brazil’s PIX or Mexico’s SPEI). These multi-tiered transaction pipelines are vulnerable to complex business logic bypasses, race conditions, and currency exchange rounding exploitation that basic vulnerability scanners never catch.
2. Florida Information Protection Act (FIPA) Compliance
Under Florida Statute § 501.171 (FIPA), commercial entities collecting customer data have a statutory obligation to maintain reasonable security safeguards. If a data breach occurs due to an unaddressed web vulnerability, organizations face strict 30-day disclosure mandates and severe civil enforcement penalties up to $500,000. Annual independent penetration testing serves as the gold standard of proof that your organization met its duty of care.
3. Real Estate and WealthTech Transaction Portals
Miami’s luxury real estate and private wealth sectors increasingly rely on bespoke client portals to handle wire transfers, KYC identity documents, and escrow communications. Threat actors frequently target these portals with Broken Object Level Authorization (BOLA) and credential stuffing attacks to divert six-figure deposit funds.
| Vulnerability Class | Miami Industry Impact | How Talon PTaaS Tests It |
|---|---|---|
| Broken Object Level Auth (BOLA) | Cross-account access in Brickell wealthtech & banking dashboards. | Multi-role authenticated autonomous runs with certified human verification. |
| Payment Logic & Race Conditions | Double-spend exploits and concurrency flaws in checkout flows. | Parallelized sub-millisecond automated fuzzing against API transaction queues. |
| GraphQL Introspection & Batching | Mass customer PII exfiltration in high-growth consumer apps. | Automated query complexity audits, batching stress-tests, and mutation bypasses. |
| Cloud IAM Boundary Escapes | Server-Side Request Forgery (SSRF) accessing cloud metadata and keys. | Active payload probing of webhook endpoints and PDF renderers. |
Moving from Outdated Consulting to Continuous PTaaS
Traditionally, Miami founders looking for a penetration test had two poor options: hire a high-overhead Big Four firm that billed $35,000+ for a slow, junior-staffed assessment, or hire a local boutique that delivered a static PDF three weeks after testing ended. By the time the PDF arrived, the engineering team had already pushed fifteen new feature releases, rendering the findings obsolete.
Talon PTaaS solves this disconnect by combining the speed of AI with the rigor of certified human penetration testers:
- 72-Hour Rapid Kickoff: Initiate testing without lengthy discovery calls or cumbersome enterprise contracting.
- Lory AI Autonomous Sweeps: Our AI pentesting engine continuously assesses your staging and production environments between human audits.
- Jira & GitHub Sync: Findings arrive directly into your engineering backlog complete with `curl` reproduction commands and code remediation recommendations.
- Unlimited 1-Click Retesting: Once your developers deploy a fix, click "Request Retest" on the dashboard. Our engineers verify the patch at no extra charge.
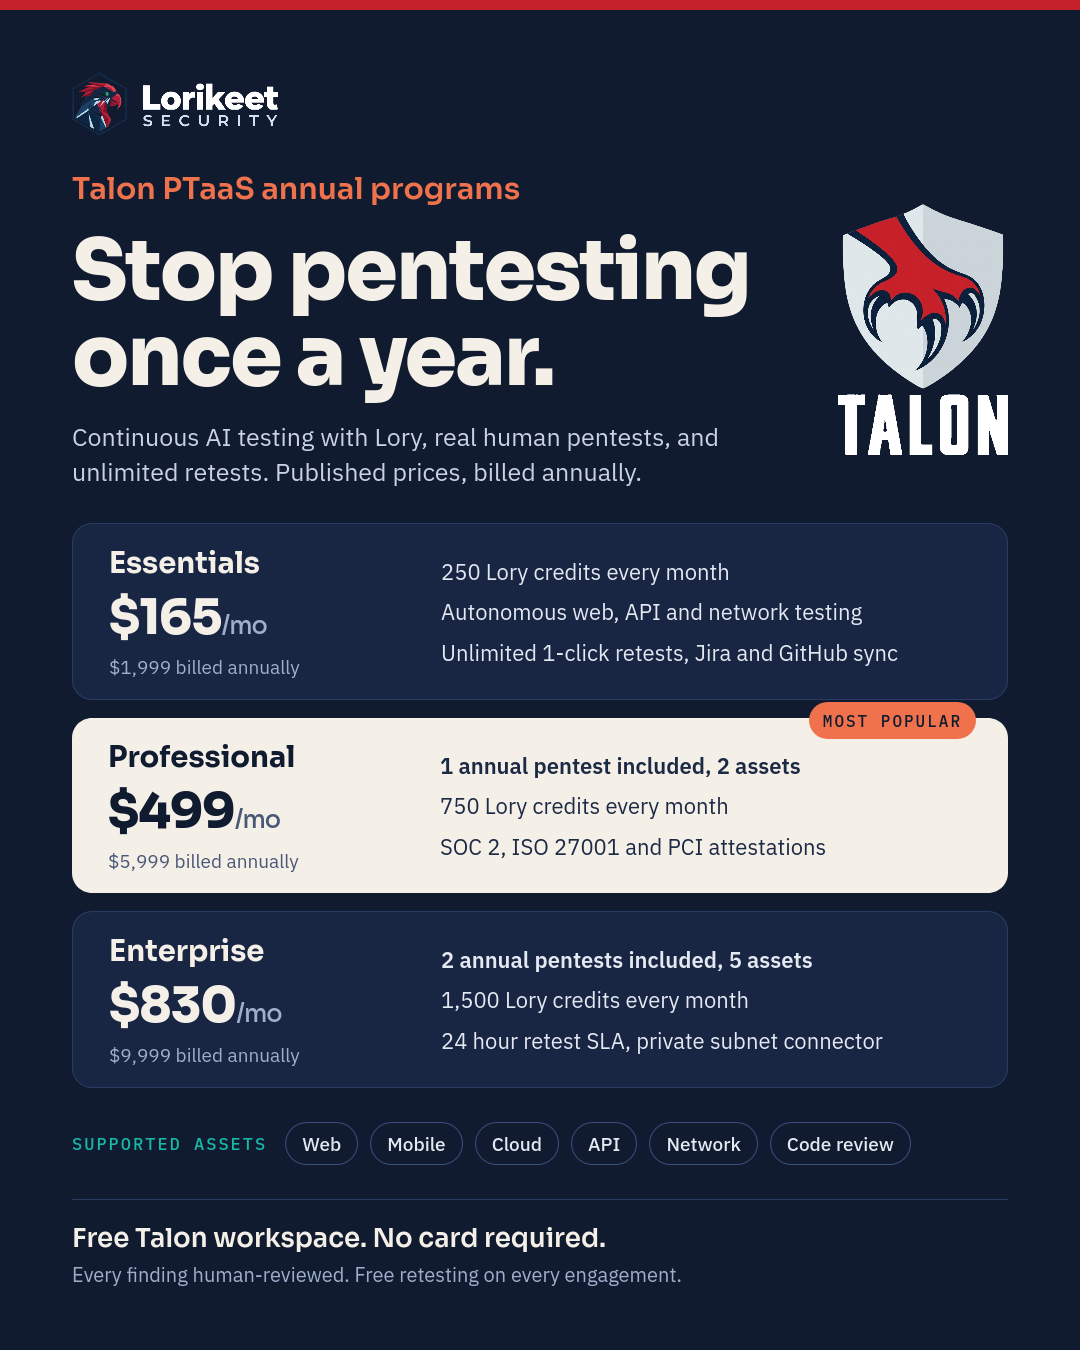
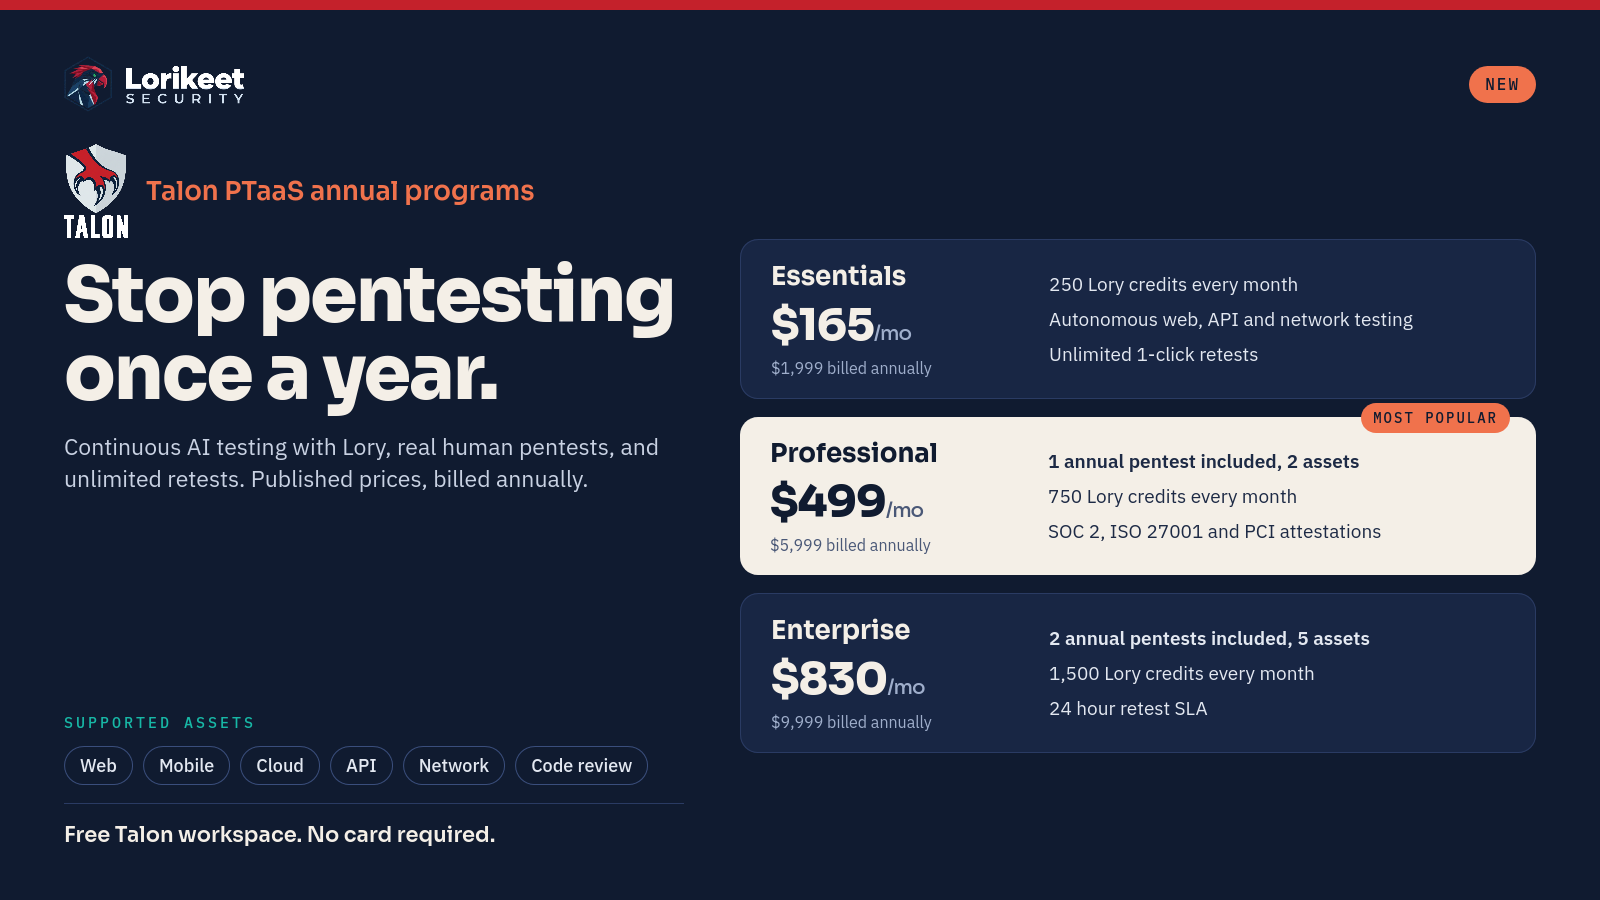
Published, Transparent Pricing: Whether you are a pre-seed startup in Wynwood building your MVP or an established Brickell financial institution, Talon offers transparent annual programs starting at $165/month ($1,990/year billed annually) with free retesting included on every engagement.
Secure Your Miami Application Stack
Upgrade to continuous PTaaS. Get transparent pricing in seconds or schedule a 15-minute scoping call with an OSCP-certified security engineer.


