
Passing SOC 2 Type II and ISO 27001 with Continuous PTaaS: The Zero-Panic Audit Strategy
Every year, hundreds of engineering and security teams experience the same gut-wrenching crisis: the Pre-Audit Scramble.
Your company's SOC 2 Type II or ISO 27001:2022 observation period ends in three weeks. The auditor sends over the evidence request list, and Item 4.2 states: "Provide third-party penetration test reports and remediation verification for all in-scope production web applications, external APIs, and cloud infrastructure covering the entire 12-month observation window."
Your heart drops. The last penetration test was conducted eleven months ago on a version of the application that has since seen forty-five production releases. Worse, the report contained two unresolved "Medium" severity authorization findings that were never retested. If your engineering team scrambles to book an emergency pentest, traditional firms quote six weeks of lead time and a $25,000 rush surcharge. A qualified audit opinion looms, threatening your active enterprise sales pipeline and board confidence.
In 2026, progressive technology companies do not subject their teams to this chaos. They have adopted the Zero-Panic Audit Strategy powered by continuous Pentest as a Service (PTaaS) on platforms like Talon.
Instead of treating offensive security as an annual emergency fire drill, continuous PTaaS operationalizes evidence collection, remediation tracking, and auditor attestations into a quiet background routine. This guide outlines how continuous offensive testing satisfies strict auditor criteria under AICPA SOC 2 and ISO/IEC 27001, details the exact control mappings, and shows how you can achieve permanent audit readiness for as little as $499/month.
The Fundamental Flaw of Snapshot Pentests in Modern Audits
To understand why the old method produces intense anxiety, one must understand how modern compliance audits actually work.
A SOC 2 Type I examination evaluates whether your controls were suitably designed on a single calendar day. In contrast, a SOC 2 Type II examination evaluates whether your controls operated effectively throughout an extended observation period—typically 6 to 12 months.
Similarly, ISO/IEC 27001:2022 Control 8.8 (Management of technical vulnerabilities) mandates that an organization obtain timely information about technical vulnerabilities, evaluate exposure, and take appropriate mitigating measures continuously.
The Auditor's Trap: If your observation window spans January 1 to December 31, and your only penetration test occurred in February, an auditor will ask: "How do you prove that major architectural changes and code deployments between March and December did not introduce critical vulnerabilities?"
With traditional annual testing, you cannot answer this question without fabricating post-hoc evidence or relying on noisy vulnerability scanner logs that lack exploit verification. With continuous PTaaS, your portal maintains a chronological, cryptographically verifiable ledger of continuous testing activity spanning every single month of the audit window.
The Four Pillars of the Zero-Panic Audit Strategy
The Zero-Panic Audit Strategy replaces episodic fire drills with four continuous operational pillars:
Autonomous AI Testing Between Assessments
Between scheduled in-depth human assessments, Lory AI continuously probes exposed perimeters, microservices, and new API routes against 57 offensive playbooks. When changes go live, security validation happens automatically.
1-Click Retesting and Verification
Developers resolve vulnerabilities directly through their normal sprint cycles using Jira/GitHub sync. A single click on the Talon dashboard queues an immediate retest. The vulnerability shifts to "Verified Fixed" within 24 to 48 hours, maintaining zero unaddressed findings on your ledger.
Auditor Read-Only Links & Instant Attestations
No more redacting 80-page PDFs by hand. You invite your auditor directly to a restricted, read-only compliance view, or generate a countersigned, tamper-evident Attestation of Penetration Testing in 1 click.
Automated Integration with Vanta, Drata & Secureframe
Talon integrates seamlessly into compliance automation engines, continuously feeding test dates, scope boundaries, and attestation letters into automated audit monitors.
Framework-by-Framework Control Mapping
Auditors don't just want a report; they want to map testing evidence to specific framework criteria. The table below demonstrates how Talon PTaaS directly satisfies the core control families for SOC 2, ISO 27001, and PCI DSS:
| Framework & Control | Auditor Expectation | How Talon PTaaS Satisfies It |
|---|---|---|
| SOC 2 CC4.1 COSO Principle 12 |
Management identifies and assesses changes that could significantly affect the system of internal control. | Continuous Lory AI probing automatically flags regressions when application routes or cloud infrastructures change. |
| SOC 2 CC7.1 System Boundaries & Vulnerabilities |
To meet its objectives, the entity uses detection and monitoring procedures to identify changes to configurations and new vulnerabilities. | Real-time finding dossiers categorize vulnerabilities with environmental CVSS 3.1 scores and exact reproduction proofs. |
| SOC 2 CC7.2 Threat Monitoring & Exploitation |
The entity monitors system components for anomalies indicative of malicious acts or vulnerabilities. | Combines certified human offensive testing with continuous external attack surface reconnaissance. |
| SOC 2 CC7.3 Remediation & Mitigation |
The entity evaluates and responds to identified security events and vulnerabilities on a timely basis. | Automated bi-directional Jira/GitHub ticket sync and 1-click retest verification confirm timely remediation. |
| ISO 27001:2022 Control 8.8 Technical Vulnerability Management |
Information about technical vulnerabilities must be obtained in a timely manner and evaluated for exposure. | Ongoing PTaaS coverage ensures zero gap between releases and offensive vulnerability identification. |
| PCI DSS 4.0 Req 11.4 Penetration Testing Methodology |
External and internal penetration tests must be performed at least once every 12 months and after any significant infrastructure/application change. | Talon provides certified annual human assessments plus targeted continuous retesting after major software releases. |
Choosing Your Compliance Tier: Talon Professional vs. Enterprise
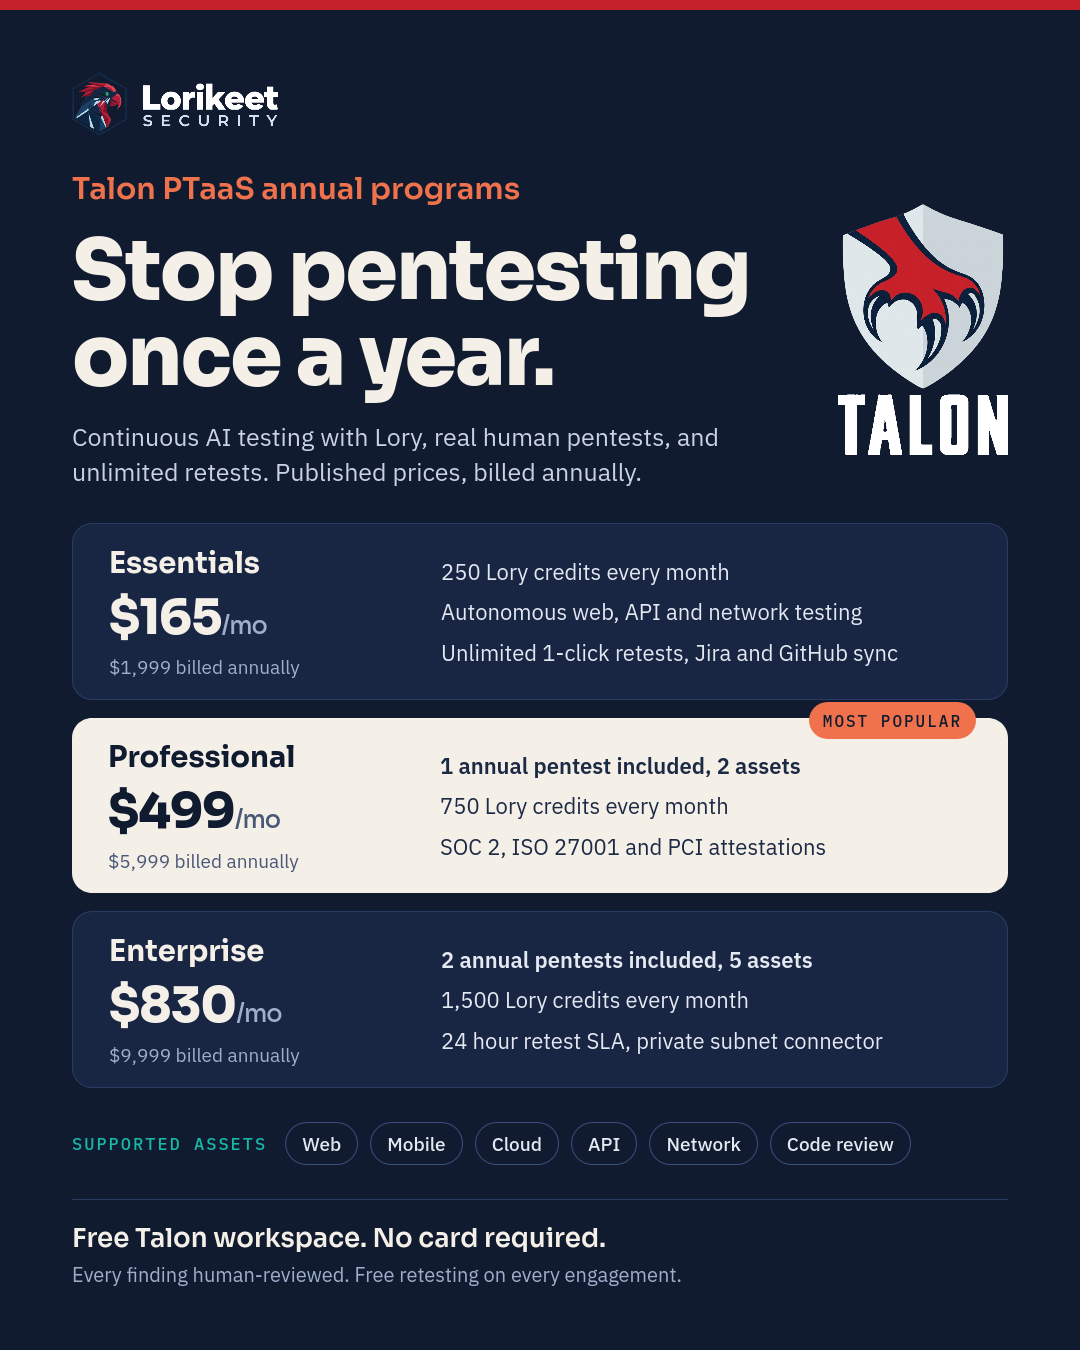
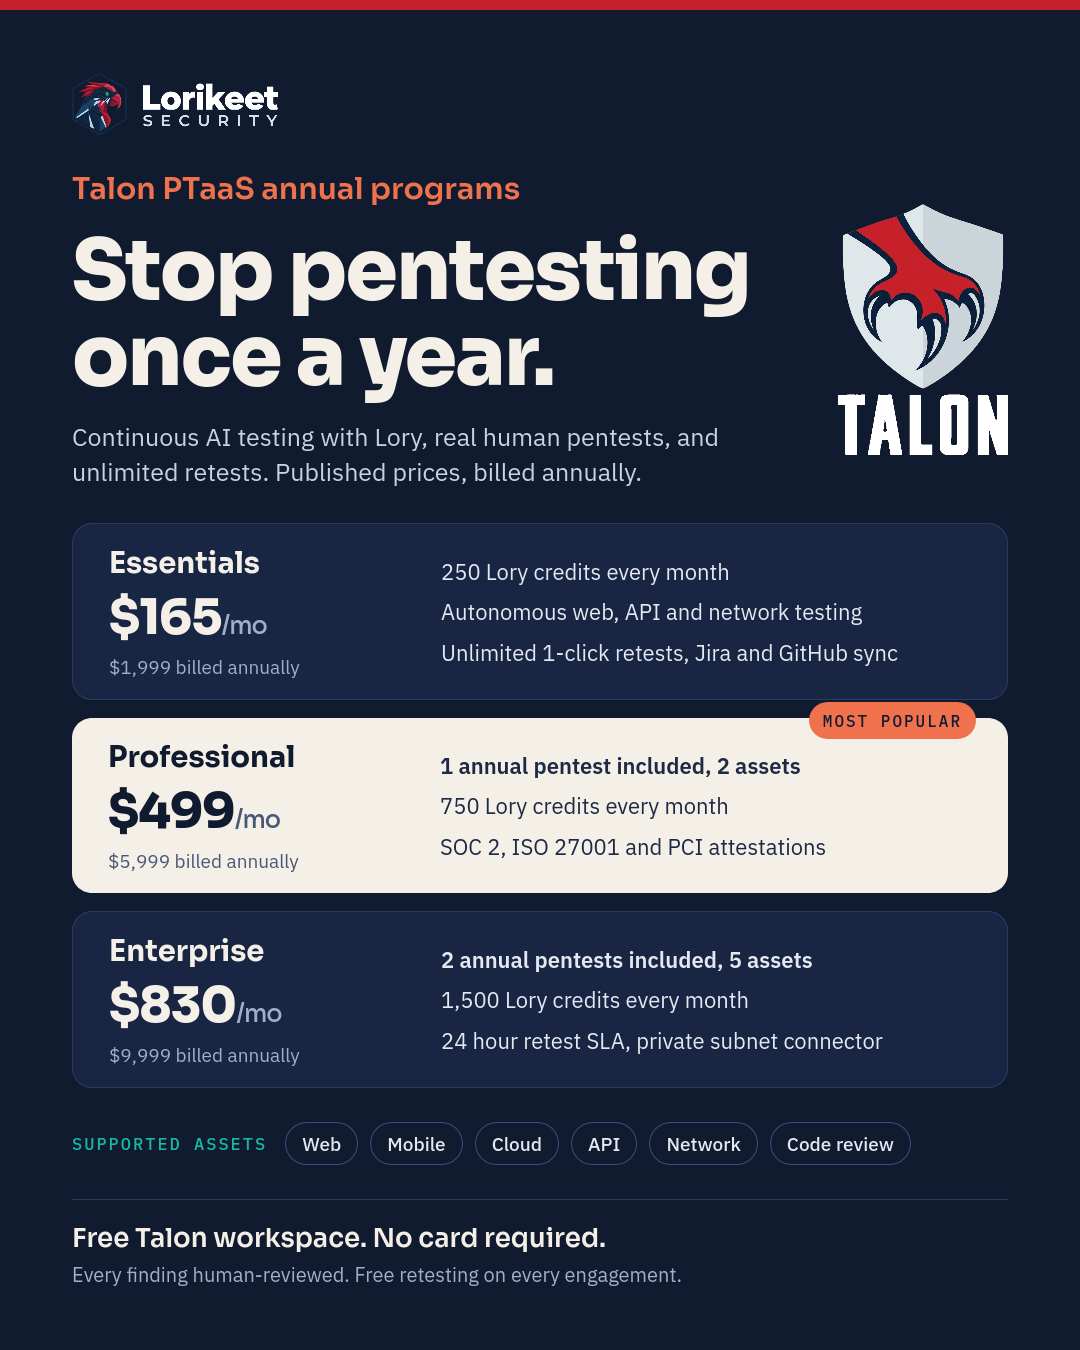
Compliance programs vary based on company scale, customer contractual obligations, and regulatory scrutiny. Lorikeet Security structures Talon PTaaS into two dedicated compliance tiers:
Talon Professional
$499 / month · $5,999 billed annually
Ideal for: B2B SaaS companies pursuing SOC 2 Type II, ISO 27001, or initial PCI DSS compliance for their primary web app and API.
- 1x Full Annual Human Pentest Included (scoped for up to 2 assets: Web App, API, Cloud).
- 750 Lory AI Credits / month for autonomous testing between assessments.
- Unlimited 1-click retest verifications.
- Auditor-Ready SOC 2, ISO 27001 & PCI Attestation Letters.
- Bi-directional Jira & GitHub synchronization.
- Dedicated lead security engineer on Slack/Teams.
Talon Enterprise
$830 / month · $9,999 billed annually
Ideal for: Multi-product companies, fintechs, and healthcare platforms with complex microservices or private VPCs.
- 2x Full Annual Human Pentests Included (scoped for up to 5 assets: Mobile, Cloud, Web, API, Code).
- 1,500 Lory AI Credits / month for deep continuous testing.
- Lory Mesh Private Subnet Connector for behind-the-firewall staging and internal VPC testing.
- Priority 24-hour retest verification SLA.
- Multi-framework attestations (SOC 2, ISO 27001, HIPAA, PCI DSS).
- Dedicated Lead Security Advisor with quarterly executive reviews.
The Zero-Panic 90-Day Pre-Audit Playbook
Follow this sequential playbook to turn your next compliance audit into an effortless non-event:
-
Day 90 Before Audit Closes — Scope & Baseline:
Verify your in-scope assets on the Talon platform (staging URLs, production endpoints, API schemas). Confirm that all microservices handling customer data are active in the target registry. -
Day 60 Before Audit Closes — Human Deep Dive & Triage:
Kick off your scheduled human penetration test. As findings populate the live dashboard, developers receive immediate tickets in Jira. Any high-severity issues are addressed in the current sprint. -
Day 30 Before Audit Closes — 1-Click Retesting:
Engineers deploy patches and click "Request Retest" on Talon. Within 24 to 48 hours, Lorikeet's security analysts verify the remediation, updating finding status to Fixed. -
Day 10 Before Audit Closes — Instant Attestation Generation:
Download your official Executive Summary and Attestation Letter directly from the Talon portal. The document contains your company's clean testing bill of health, methodologies mapped to NIST SP 800-115 and OWASP ASVS, and tester credentials. -
Audit Day — Zero Panic:
Upload the Attestation Letter to your compliance platform (Vanta, Drata) or grant your auditor a read-only login link. Your auditor gets exactly what they need in seconds, with zero questions asked.
Auditor Secret: Compliance auditors hate reading 90-page raw technical pentest reports as much as you hate requesting them. What auditors actually want is a signed Attestation Letter from an accredited third-party certifying that testing occurred, findings were triaged, and critical remediations were verified. Talon gives auditors exactly what they need.
Never Stress Over a Compliance Pentest Again
Join hundreds of fast-growing technology companies who have switched to Talon PTaaS. Get transparent pricing, instant auditor attestations, and continuous security peace of mind.


