
The Toronto-Waterloo tech ecosystem has established itself as one of the most prolific software hubs in North America. From enterprise B2B SaaS platforms operating out of the MaRS Discovery District to generative AI companies in King West, Canadian technology startups are competing on the global stage. However, as soon as a Canadian SaaS startup attempts to close its first six-figure enterprise contracts with US Fortune 500 or European enterprise buyers, it encounters an uncompromising roadblock: the enterprise vendor security review.
While compliance with the Canadian federal Personal Information Protection and Electronic Documents Act (PIPEDA) and provincial regulations like Ontario's PHIPA or Quebec's Law 25 is mandatory domestically, international buyers require formal third-party audit reports. Specifically, SOC 2 Type II and ISO/IEC 27001:2022 are mandatory table stakes. And at the absolute center of both audit frameworks is one critical technical requirement: independent, third-party penetration testing.
The Canadian Startup Dilemma: Legacy Consulting vs. High-Velocity Shipping
Historically, Toronto founders facing SOC 2 compliance were forced into an expensive, inefficient consulting model. Traditional Canadian consulting firms and Big Four practices quote between $25,000 and $45,000 CAD for a standard point-in-time penetration test. Worse, the process takes four to eight weeks to schedule, delivers a 50-page static PDF report that offers little practical help to engineers, and charges thousands of dollars in "retest change orders" just to verify that patches work.
For modern engineering teams in Toronto shipping code multiple times a week to AWS Canada (Central) or multi-region GCP clusters, this annual ritual creates severe friction:
- 364 Days of Blind Spots: An annual point-in-time pentest is out of date the minute new code deploys to staging or production.
- The Observation Window Trap: In a SOC 2 Type II audit, auditors examine controls across a 3 to 12-month observation window. If an unaddressed critical vulnerability persists without verified remediation, it can trigger a qualified audit opinion.
- Developer Velocity Bottlenecks: PDFs filled with generic scanner output create animosity between security compliance leads and software developers.
| Capability / Metric | Traditional Canadian Consulting | Talon Continuous PTaaS |
|---|---|---|
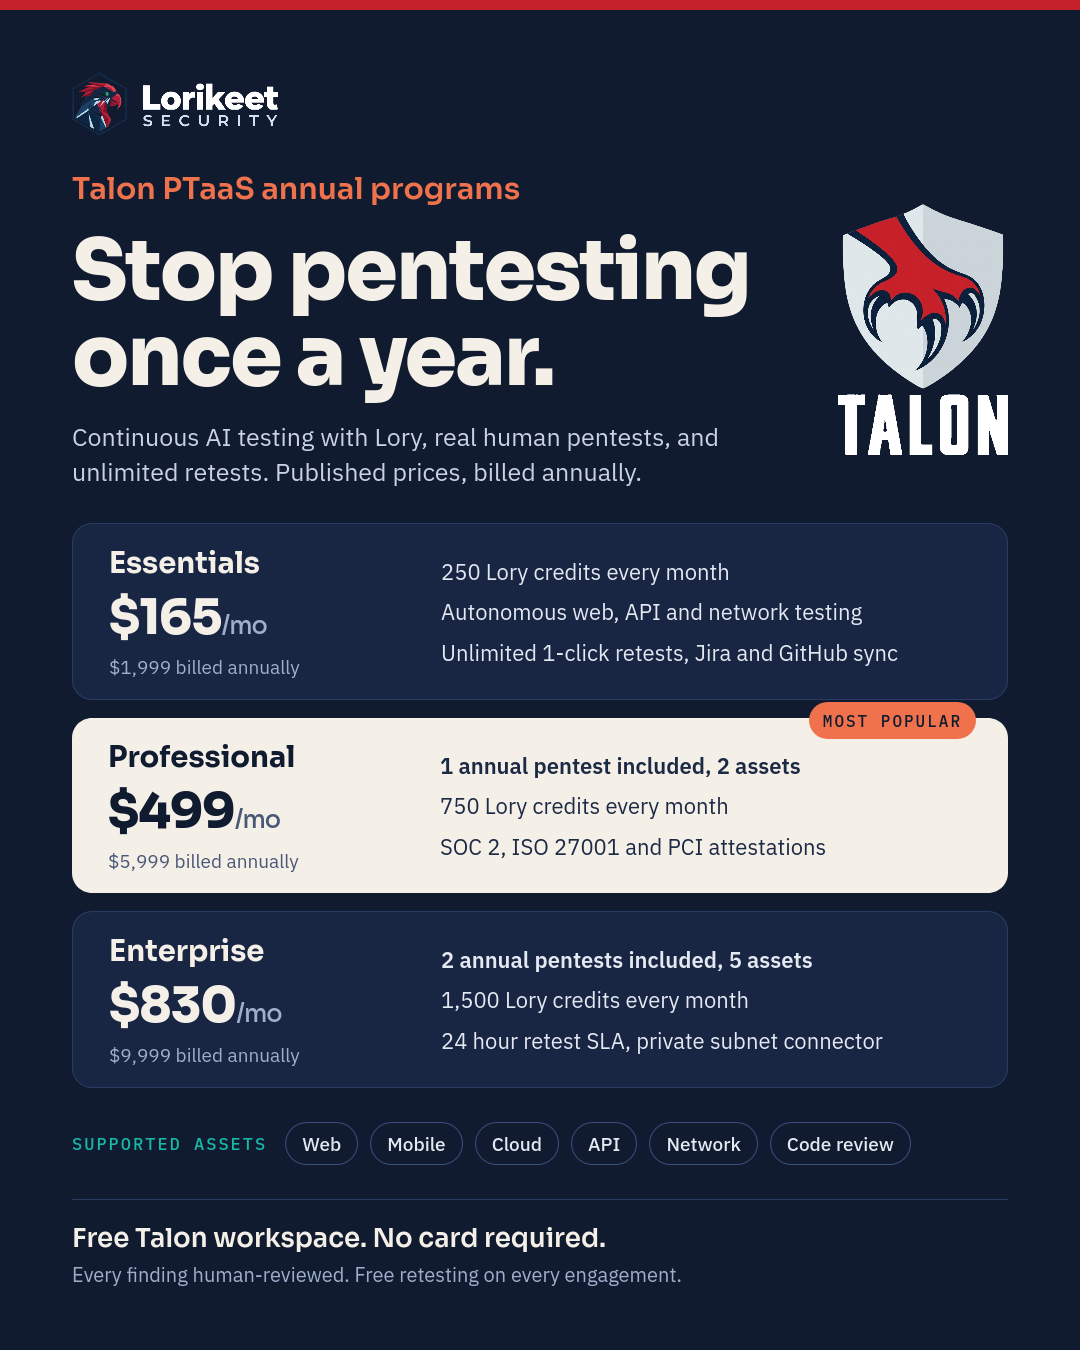
| Pricing Model | $25,000 – $45,000 CAD per single test | Published subscription from $165 to $830 USD/mo |
| Cadence | Point-in-time (annual snapshot) | Continuous AI autonomous runs + scheduled deep tests |
| Retest Verification | $2,500 – $5,000 fee per retest | Unlimited 1-Click Retests Included |
| Auditor Integration | Manual email attachments | 1-click Attestation Letters & Vanta/Drata sync |
| Developer Experience | Static PDF reports | Bi-directional Jira, GitHub Issues, and AI IDE MCP sync |
Mapping Penetration Testing to SOC 2 and ISO 27001 Controls
To pass an audit without stress, security leads must map technical findings directly to specific framework controls:
SOC 2 Trust Services Criteria
- CC4.1 (COSO Principle 12): The entity selects, develops, and performs ongoing and/or separate evaluations to ascertain whether the components of internal control are present and functioning.
- CC7.1: To meet its objectives, the entity uses detection and monitoring procedures to identify changes to configurations and new vulnerabilities.
- CC7.3 & CC7.4: The entity evaluates security incidents and implements corrective actions to remediate vulnerabilities and verify remediation effectiveness.
ISO/IEC 27001:2022 Controls
- Control 8.8 (Management of Technical Vulnerabilities): Requires organizations to obtain information about technical vulnerabilities, evaluate exposure, and implement appropriate measures to address them.
- Control 8.25 (Secure Development Lifecycle): Rules for the secure development of software and systems should be established and applied, including verification testing.
- Control 5.37 (Documented Operating Procedures): Operating procedures for information processing facilities must be documented and maintained.
The 90-Day Pre-Audit Playbook for Toronto Startups
By shifting to Talon PTaaS, high-growth startups can follow a streamlined 90-day playbook before their SOC 2 or ISO audit window closes:
- Day 1–15: Asset Scoping & Baseline Autonomous Sweep: Connect your web apps, APIs, and cloud perimeters to Talon. Lory AI initiates continuous Layer 3/Layer 4 reconnaissance and non-destructive autonomous probing.
- Day 16–45: Deep Human Pentest & Remediation Sprint: Certified OSCP/CISSP security engineers conduct deep multi-stage exploitation against business logic, authorization boundaries (BOLA/IDOR), and cloud configurations. Findings sync automatically into Jira or Linear.
- Day 46–60: Instant 1-Click Retesting: As developers ship PRs, they click "Request Retest" in Talon. Verified fixes transition to "Fixed" with a cryptographic audit trail.
- Day 61–90: Auditor Attestation Package: Generate your official, countersigned Attestation of Penetration Testing directly from Talon and export it into Vanta, Drata, or directly to your audit team.
Canadian Data Residency & Sovereignty: Lorikeet Security maintains dedicated Canadian infrastructure hubs in Toronto and Calgary, ensuring that client metadata, scoped scans, and credentials stay compliant with Canadian data sovereignty expectations.
Accelerate Your SOC 2 & ISO 27001 Readiness
Don't let enterprise sales stall behind compliance reviews. Get continuous testing, 1-click retests, and auditor-ready reports starting at just $165/month.


